DevSecOps and Secure CI/CD Consulting

Let's Talk
  • PROTECT YOUR CODE

    Scans for code flaws, vulnerable dependencies and leaked secrets run on every pull request, with results shown where developers already work.

  • PROTECT YOUR PIPELINE

    Build runners, credentials and third-party actions are locked down, so a compromised dependency can’t reach production on its own.

  • PROTECT YOUR RELEASES

    Signed artifacts, SBOMs and policy gates show exactly what was shipped and give you evidence ready for audits.

Why It Matters

Racing to Deliver While Staying Secure? We’ve Been There.

Most delivery teams already run some security tools. The results sit in a separate dashboard, findings pile up, and the pipeline itself holds long-lived keys with access to production. Attackers have noticed: compromised build tools and third-party CI actions have become a direct route into software supply chains. We embed security checks where developers work, harden the pipeline itself, and tune the process so it protects releases instead of blocking them.

Modernizing unstable systems? Launching new products?

We build development environments that deliver enterprise-grade scalability, compliance-driven security, and control baked in from day one.

Check Our Portfolio
What We Offer

Services We Provide

  • DevSecOps Strategy

    Transform Your Development Pipeline! 

    Most teams already own some security tools. The gaps are usually in coverage, ownership, and what happens to the findings. That is where we start.

    Here’s how we can help:

    • Maturity assessment. We assess your current practices against OWASP SAMM or the OWASP DevSecOps Maturity Model, covering tooling, process, and ownership. You get a scored baseline and a roadmap of what to improve first.
    • Strategy and ownership. We define who owns each control, how findings are triaged, and which issues block a release. Security stops depending on one person remembering to check.
    • Tooling selection and rollout. We choose tools that fit your stack, from open-source scanners to commercial platforms, and roll them out without flooding developers with noise. Every tool we add has an owner and a defined action for its findings.
  • Secure CI/CD Pipeline Implementation

    The pipeline is part of your attack surface. Build runners hold deployment credentials, and a single compromised third-party action, as in the tj-actions/changed-files incident in 2025, can expose secrets across thousands of repositories. We secure both what the pipeline checks and the pipeline itself.

    Find out how we secure your CI/CD pipeline here:

    • CI/CD platform hardening. We pin third-party actions and plugins to commit hashes, restrict runner and token permissions, protect branches, and replace long-lived cloud keys with short-lived OIDC credentials. We use the OWASP Top 10 CI/CD Security Risks as the baseline.
    • Pipeline design and automation. We design pipelines where security checks run automatically at the right stage: fast checks on every pull request, deeper scans before release. The same rules apply to every service and every team.
    • Security testing in the pipeline. We integrate and tune the checks your codebase needs:
      • SAST (Static Application Security Testing) for code analysis.
      • DAST (Dynamic Application Security Testing) for runtime testing.
      • IAST (Interactive Application Security Testing) for hybrid analysis.
      • SCA (Software Composition Analysis) for vulnerable and outdated dependencies.
      • Container image scanning for vulnerable packages in base images.
    • Security regression tests. Tests for authentication, authorization, and input handling run alongside your unit and integration tests. A fixed vulnerability stays fixed.
    • Infrastructure as Code security. Terraform, CloudFormation, Helm charts, and Kubernetes manifests are scanned with tools such as Checkov or Trivy before they are applied. Misconfigurations are caught in the pull request, not in production.
    • Secrets management. Credentials move into HashiCorp Vault, AWS Secrets Manager or Azure Key Vault; every commit is checked for leaked secrets, and anything already exposed in Git history is rotated.
  • Developer Security Training

    Let’s strengthen your Human Firewall.

    Here’s how we prepare your workforce:

    • DevSecOps training. Hands-on sessions for developers and platform engineers on reading scanner results, fixing findings, and keeping the pipeline secure. Training uses your own stack and real findings from your codebase.
    • Secure coding training. Developers learn to prevent injection, broken access control, insecure authentication, and misconfigurations, based on the OWASP Top 10 and examples in the languages they use every day.
    • Threat modeling workshops. We run threat modeling sessions with your team for new features and architecture changes. Risks are discussed at the design stage, when they are cheapest to fix.
  • Software Supply Chain Security

    Attackers increasingly target dependencies and build systems instead of the application itself. We make every release traceable from source code to the running artifact.

    • SBOM generation. Every build produces a software bill of materials in CycloneDX or SPDX format. When a new vulnerability is disclosed, you immediately see which products and versions contain the affected component.
    • Artifact signing and provenance. Container images and build artifacts are signed with Sigstore Cosign, with build provenance aligned with the SLSA framework. Your clusters accept only artifacts built and signed by your pipeline.
    • Dependency hygiene. Lockfiles, private package registries, and rules against typosquatted or newly published packages reduce the chance of a malicious dependency entering the build.
    • Regulatory readiness. The same setup covers SBOM and vulnerability handling requirements under the EU Cyber Resilience Act and US federal software procurement.
  • Vulnerability Management and Remediation

    Scanners produce findings. The value lies in triaging them, fixing what matters, and proving it was fixed.

    • Embedded scanning. We integrate tools such as SonarQube, Snyk, or GitLab security scanners into your pipeline. Every pull request is checked for vulnerabilities in code, dependencies, and configurations, with results shown as review comments.
    • Automated remediation. Dependabot or Renovate opens pull requests for vulnerable dependencies, and base images are rebuilt when patched versions come out. Fixes go through the same review and tests as any other change.
    • Risk-based prioritization. Findings are deduplicated and ranked by severity, known exploitation in the CISA KEV catalog, EPSS score, and whether the vulnerable code is reachable in production. Each finding is tracked to closure with an owner, so critical issues don’t sink in a backlog of low-risk noise.
  • Cloud Security Integration

    Containers, Kubernetes, and serverless functions add layers that application scanners don’t see. We cover them from build to runtime.

    • Kubernetes and container security. We enforce Pod Security Standards, network policies, and admission rules for Kubernetes, and detect suspicious runtime behavior with tools such as Falco or Aqua Security. Workloads run with the minimum privileges they need.
    • Cloud Security Posture Management. Platforms such as Wiz, Prisma Cloud, or Orca Security continuously check your cloud accounts for misconfigurations, exposed resources, and excessive permissions. Findings are mapped to CIS Benchmarks, NIST, and SOC 2 controls.
    • Runtime detection and response. Runtime sensors and cloud audit logs raise alerts on suspicious activity in virtual machines, containers, and serverless functions. Response playbooks isolate affected workloads and preserve evidence for investigation.
  • Compliance and Governance

    Automated checks in the pipeline produce that evidence with every release.

    Our customized approach includes:

    • Policy as code. Rules written in Open Policy Agent, HashiCorp Sentinel, or AWS Config check infrastructure and deployments against SOC 2, HIPAA, and PCI DSS controls on every change. A non-compliant configuration fails the pipeline before it reaches production.
    • Audit trail. Every deployment, approval, configuration change, and security finding is logged in Elastic Stack or Splunk. Your team can show auditors who changed what, when, and with whose approval.
    • Governance policies. We write secure development, access control, and incident response policies that match how your teams actually work. Each policy is backed by a pipeline control, so it is enforced rather than just documented.
  • Continuous Monitoring and Improvement

    A secure pipeline needs ongoing attention as services, dependencies, and threats change.

    • Security metrics. Dashboards in Grafana or Kibana track time to fix critical findings, scan coverage across repositories, and the share of builds passing policy gates. Leadership sees whether security is improving, not just how many findings exist.
    • Regular reviews. We review scanner results, false-positive rates, and incident findings on a regular schedule and adjust rules and priorities. The pipeline adapts to new threats and regulations instead of drifting out of date.
    • Threat detection and incident response. Alerts from Splunk, Elastic Security, or Microsoft Sentinel are correlated with pipeline and deployment events. After every incident, a blameless post-mortem turns findings into new pipeline controls.
DevSecOps phases

Our DevSecOps Approach

01.

01. Assess the Current Pipeline

We review your repositories, CI/CD configuration, build runners, artifact storage and deployment paths, along with how secrets and permissions are handled. You get a map of where security checks exist today and where code can reach production without them.

02.

02. Threat-Model the Delivery Chain

We identify how an attacker could tamper with code, dependencies, build steps or deployment credentials, using the OWASP Top 10 CI/CD Security Risks as a baseline. Each risk is ranked by impact and likelihood.

03.

03. Prioritize and Plan

Findings become a roadmap that balances risk reduction with developer friction. High-impact fixes such as removing long-lived credentials come first, followed by tooling and policy changes.

04.

04. Implement Controls in the Pipeline

We add scanning, secrets management, signing and policy checks step by step. New checks start in warning mode and become blocking once false positives are tuned out, so developers trust the results instead of ignoring them. 05

05.

05. Measure and Hand Over

We track metrics such as time to fix critical findings and the share of builds passing policy gates. Your team receives runbooks and training to own and extend the setup.

  • 01. Assess the Current Pipeline

  • 02. Threat-Model the Delivery Chain

  • 03. Prioritize and Plan

  • 04. Implement Controls in the Pipeline

  • 05. Measure and Hand Over

How We Can Strengthen Your Delivery

Choose the Setup That Fits Your DevSecOps Goals

01

Discovery Sprint

We find the gaps before we change the pipeline.

We review how your delivery process works today. We look at where security enters the lifecycle and where it still depends on manual checks.

From there, we define the DevSecOps roadmap. You get clear priorities and a practical implementation plan your team can act on.

Good fit when: You know security needs to move earlier in the lifecycle but need a clear starting point.

Read more
02

Project-Based Delivery

We secure the pipeline end to end.

For a defined scope, we own the implementation. That can include pipeline hardening and automated security checks. It can also cover secrets handling or infrastructure security.

You stay involved in the decisions that affect your engineering process. We manage the work through rollout and validation.

Good fit when: You want a secure CI/CD setup delivered as a complete project rather than a list of recommendations.

Read more
03

Dedicated Team

We stay with the pipeline as it evolves.

DevSecOps does not stop after the first implementation. New services change the attack surface. New environments create different risks. Compliance requirements evolve too.

A dedicated team gives you stable capacity to keep improving the setup. The same people stay close to the system and build working knowledge over time.

Good fit when: Secure delivery is an ongoing engineering priority across several products or teams.

Read more
04

Build-Operate-Transfer (BOT)

We build the DevSecOps function. You bring it in-house.

We assemble the team and run it while the operating model takes shape. The team establishes delivery practices and builds working knowledge of your environment.

Once the setup is stable, the team transfers to your organization. The knowledge stays with the people who built the function.

Good fit when: You want a permanent internal DevSecOps capability but do not want to build it from zero.

Read more
05

Staff Augmentation

You run the process. We add DevSecOps depth.

If your delivery model is already working, we add experienced engineers where your team needs more capacity.

They join your existing process and work inside your stack. You keep control of priorities and delivery.

Good fit when: You already know what needs to be done and need stronger execution capacity.

Read more
Case Studies

Our Latest Works

View All Case Studies
Juriba Juriba
  • Backend
  • Frontend
  • Cloud
  • DevOps & Infrastructure

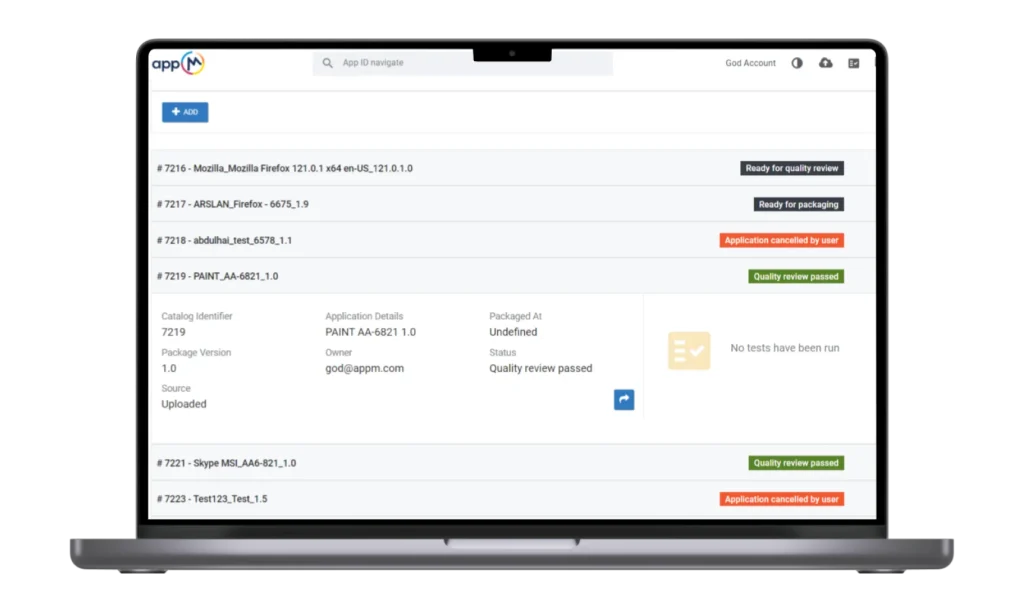
Juriba: Enterprise Digital Workplace Management Platform for Migration & Automation

An enterprise-grade automation platform that streamlines IT project workflows through smart dashboards.

Additional Info

Core Tech:
  • .NET 6
  • MS SQL
  • Redis
  • Angular
  • NgRx
  • RxJS
  • Kubernetes
  • Elasticsearch
Country:

United Kingdom United Kingdom

Web 3 White-label PaaS NeoBank Web 3 White-label PaaS NeoBank
  • Web3
  • Fintech

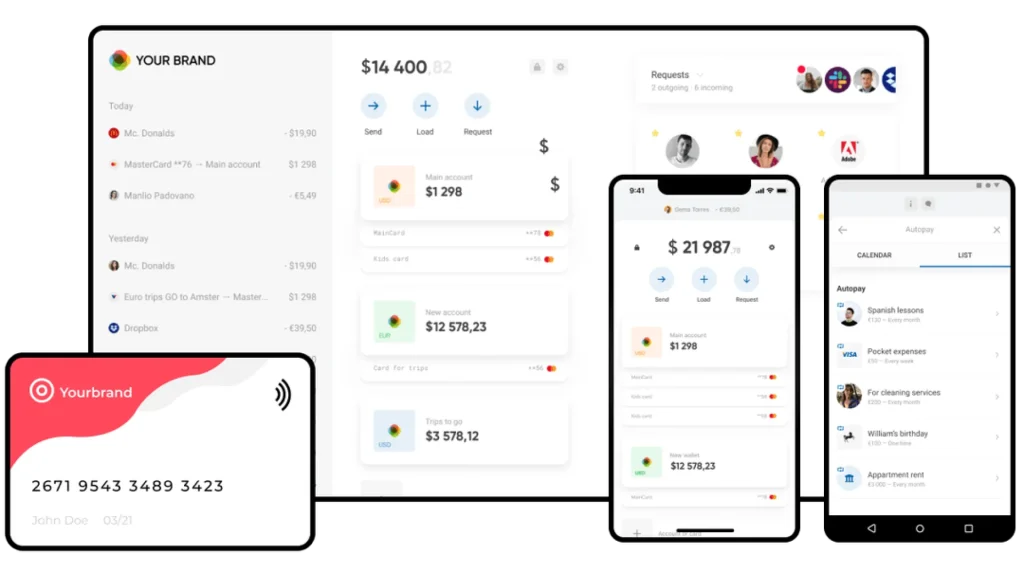
Web3 PaaS Ecosystem for Next-Gen NeoBanking, RegTech, and Secure Data Vaulting

A blockchain-powered PaaS ecosystem enabling financial providers to launch custom neobanking solutions with secure infrastructure.

Additional Info

Core Tech:
  • Blockchain
  • .NET
  • Node.js
  • AWS
  • Docker
  • PostgreSQL
  • React Native
Country:

USA USA

Trading System for Confidential Market Execution Trading System for Confidential Market Execution
  • Fintech
  • ATS

Trading System for Confidential Market Execution

A fintech trading system enabling anonymous, low-impact transactions between institutional players.

Additional Info

Core Tech:
  • .NET Core
  • Kafka
  • Redis
  • React.js
  • WebSockets
  • OAuth 2.0
  • PostgreSQL
  • Selenium
Country:

USA USA
Testimonials

Testimonials

Carl-Fredrik Linné                                            Sweden

The solutions they’re providing is helping our business run more smoothly. We’ve been able to make quick developments with them, meeting our product vision within the timeline we set up. Listen to them because they can give strong advice about how to build good products.

Darrin Lipscomb Darrin Lipscomb
Darrin Lipscomb United States

We are a software startup and using Devox allowed us to get an MVP to market faster and less cost than trying to build and fund an R&D team initially. Communication was excellent with Devox. This is a top notch firm.

Daniel Bertuccio Daniel Bertuccio
Daniel Bertuccio Australia

Their level of understanding, detail, and work ethic was great. We had 2 designers, 2 developers, PM and QA specialist. I am extremely satisfied with the end deliverables. Devox Software was always on time during the process.
Trent Allan Trent Allan
Trent Allan Australia

We get great satisfaction working with them. They help us produce a product we’re happy with as co-founders. The feedback we got from customers was really great, too. Customers get what we do and we feel like we’re really reaching our target market.

Andy Morrey                                            United Kingdom

I’m blown up with the level of professionalism that’s been shown, as well as the welcoming nature and the social aspects. Devox Software is really on the ball technically.

Vadim Ivanenko Vadim Ivanenko
Vadim Ivanenko Switzerland

Great job! We met the deadlines and brought happiness to our customers. Communication was perfect. Quick response. No problems with anything during the project. Their experienced team and perfect communication offer the best mix of quality and rates.

Jason Leffakis Jason Leffakis
Jason Leffakis United States

The project continues to be a success. As an early-stage company, we're continuously iterating to find product success. Devox has been quick and effective at iterating alongside us. I'm happy with the team, their responsiveness, and their output.

John Boman John Boman
John Boman Sweden

We hired the Devox team for a complicated (unusual interaction) UX/UI assignment. The team managed the project well both for initial time estimates and also weekly follow-ups throughout delivery. Overall, efficient work with a nice professional team.

Tamas Pataky Tamas Pataky
Tamas Pataky Canada

Their intuition about the product and their willingness to try new approaches and show them to our team as alternatives to our set course were impressive. The Devox team makes it incredibly easy to work with, and their ability to manage our team and set expectations was outstanding.

Stan Sadokov Stan Sadokov
Stan Sadokov Estonia

Devox is a team of exepctional talent and responsible executives. All of the talent we outstaffed from the company were experts in their fields and delivered quality work. They also take full ownership to what they deliver to you. If you work with Devox you will get actual results and you can rest assured that the result will procude value.

Mark Lamb Mark Lamb
Mark Lamb United Kingdom

The work that the team has done on our project has been nothing short of incredible – it has surpassed all expectations I had and really is something I could only have dreamt of finding. Team is hard working, dedicated, personable and passionate. I have worked with people literally all over the world both in business and as freelancer, and people from Devox Software are 1 in a million.

Insights

Our Experts' Insights

Fortifying the Future: Ensuring Data Security in SaaS Applications

Security Best Practices In Fintech Application Development

Healthcare Web Development In 2023: A Complete Guide

FAQ

Frequently Asked Questions

  • What is DevSecOps?

    DevSecOps is the practice of building security into every stage of software delivery, from code review and builds to deployment and runtime, instead of checking it at the end. In practice, it means automated security checks in the CI/CD pipeline, clear ownership of findings and a pipeline that is itself protected against tampering. Our consulting covers strategy, implementation, training and ongoing improvement.

  • We already have a security team and tools. Why bring in external consultants?

    Pipeline security often falls between the security team and platform engineering, and neither has time to own it fully. We bring hands-on experience with CI/CD attack paths, tool tuning and supply chain controls, work alongside your team and leave the setup documented so your people own it afterward.

  • How does this impact our delivery timelines and product release cycles?

    Done well, it removes late-stage surprises rather than adding friction. We introduce new checks in warning mode, tune out false positives, and only then let critical findings block a merge. Fast scans run on every pull request, while slower tests such as DAST run on a schedule or before release.

  • How does DevSecOps consulting benefit the end users of our product?

    Your users get software with fewer exploitable vulnerabilities and faster fixes when new issues are disclosed. For B2B products, the evidence from your pipeline, such as SBOMs, scan reports, and signed releases, also answers the security questionnaires customers send during procurement.

  • We are a small team with a limited budget. Is DevSecOps consulting worthwhile for us?

    Yes. Small teams benefit most from automation because nobody has time to check security manually. We start with open-source tools such as Semgrep, Trivy and Gitleaks plus the security features already built into your CI/CD platform, and focus on the few controls that remove the most risk.

  • We’re focusing on scaling right now. Shouldn’t security come later?

    Security is easier to add while the pipeline is small. Every new service, environment and team adds credentials and dependencies that would otherwise need securing retroactively. A basic baseline now, covering secrets, dependency scanning and pipeline permissions, keeps that work from piling up and makes your first enterprise security review much easier.

  • How can DevSecOps consulting services improve our CI/CD pipeline?

    Vulnerabilities, leaked secrets and misconfigurations are caught in pull requests instead of in production. The pipeline stops holding long-lived credentials, every release is traceable to the code and dependencies it contains, and you get the evidence auditors and enterprise customers ask for.

Book a call

Want to Achieve Your Goals? Book Your Call Now!

Contact Us

We Fix, Transform, and Skyrocket Your Software.

Tell us where your system needs help — we’ll show you how to move forward with clarity and speed. From architecture to launch — we’re your engineering partner.

Book your free consultation. We’ll help you move faster, and smarter.

Let's Discuss Your Project!

Share the details of your project – like scope or business challenges. Our team will carefully study them and then we’ll figure out the next move together.


    By sending this form I confirm that I have read and accept the Privacy Policy

    Thank You for Contacting Us!

    We appreciate you reaching out. Your message has been received, and a member of our team will get back to you within 24 hours.

    In the meantime, feel free to follow our social.


      Thank You for Subscribing!

      Welcome to the Devox Software community! We're excited to have you on board. You'll now receive the latest industry insights, company news, and exclusive updates straight to your inbox.