


- ECU Threat Modeling Sprint. The team treats every ECU as a separate risk scenario, defining critical attack vectors and safety impacts.
- Zonal Architecture Attack Path Mapping. We map attack paths through zonal controllers, domains, and Automotive Ethernet. This analysis pinpoints critical transition points between domains where an attacker pivots between domains — and goes fleet-wide.
- TARA Workflow Automation Setup. We deploy a structured TARA pipeline—from component data collection to risk finalization. By integrating tools into your development processes, TARA rides with your release train instead of gating it.
- Threat-Centric Risk Analytics Dashboard. We build a dashboard that visualizes risks across the SDV ecosystem for technical leadership. Technical executives can quickly identify threats that require action and plan mid-term security roadmaps.
- Continuous TARA Update Loop. We configure a TARA update loop for changes in code, architecture, or emerging vulnerabilities. The system flags specific analysis areas for review.
Auto Cybersecurity Services
-
CLAIM THE MARKET
Launch new SDV revenue streams without widening the attack surface that comes with them. -
SHIP WITH CONFIDENCE
Deliver every SDV release through a hardened architecture that holds steady under real production pressure.
-
GOVERN EVERY SYSTEM
See every ECU, domain, and OTA channel in one operating picture — and govern who can touch what.
Why choose Devox Software?
What We Offer
Zero-Downtime Legacy Modernization
Rather than one risky, expensive cutover, we break monolithic architectures into services and move automotive backends to the cloud in controlled stages — security controls intact at every step.
Scalable OTA Pipelines
We design and build OTA update infrastructure that holds at fleet scale. We build cloud architectures that reduce package size, shorten installation windows, and include rollback strategies and update provenance verification.
Converged IT/OT Infrastructure Observability
We connect fragmented IT and OT systems into one observable platform. We build real-time architectures that link IT backends with the OT layer, reducing supplier-driven complexity and creating end-to-end product visibility.
What We Deliver
Services We Provide
-
SDV Threat Assessment
-
SBOM Assurance
- Full-Stack SBOM Reconstruction. The team traverses the entire software stack—from ECUs to cloud backends—to form a complete dependency map. We account for third-party libraries, including the transitive dependencies internal reviews never see.
- Vulnerability Correlation Engine. We build a mechanism that correlates the SBOM with current CVEs, scores each one by CVSS and blast radius, down to the affected ECU.
- Dependency Health Monitoring. We set up a monitoring process for dependency changes, new versions, and potential conflicts. The system signals risks during updates or when integrating new components into the SDV architecture.
- Remediation Roadmap Builder. We develop a step-by-step remediation roadmap based on priority, functional impact, and implementation complexity. This provides leadership with a clear strategy to reduce risks in critical domains first.
- Continuous SBOM Sync Loop. We implement a process that automatically updates the SBOM after code, firmware, or architecture changes. This keeps data relevant during SDV function releases and maintains supply chain transparency.
-
Zonal Architecture Hardening
- Zonal Controller Security Blueprint. We create a detailed zonal controller blueprint that analyzes interactions, data-transmission channels, and domain transition points.
- Automotive Ethernet Traffic Integrity Review. We conduct an in-depth analysis of Automotive Ethernet traffic, including high-speed streams from sensors, cameras, and LiDARs. Our team verifies authentication, routing, and data processing mechanisms to secure critical SDV channels.
- Domain Isolation & Lateral Movement Control. We develop a domain isolation model that accounts for real-world attack-movement scenarios within the SDV architecture. The team defines how a threat can move from infotainment to ADAS or telematics and creates technical barriers to contain the spread of incidents.
-
Smart Cockpit Protection
- Voice Interface Safety Testing. The team verifies voice system behavior during complex interaction scenarios, testing reactions to adversarial inputs and injection attempts. We determine how the interface maintains safety under real-world conditions.
- Connected App Behavior Analysis. We analyze application behavior within the smart cockpit environment. We evaluate API interactions and cloud data transmission to pinpoint which integrations require additional security controls.
- Infotainment API Interaction Review. We map interactions between infotainment and backend services. Our analysis evaluates request processing, authentication, and system behavior under peak loads to identify vulnerabilities in data-exchange logic.
- Payment Module Integrity Check. We secure functions that manage sensitive financial data. With audited transaction logic and encryption, we keep your payment processing isolated, preventing unauthorized access while shielding vehicle controls from financial-layer risks.
- Smart Cockpit Stress Simulation. We test cockpit resilience through real-world usage and anomaly simulations. This identifies sources of latency and instability early.
-
Fleet Operational Resilience
- Fleet Exposure Mapping. We provide full visibility into interactions across the fleet ecosystem. By identifying penetration paths and critical lockout risks, you know what to shield first.
- Fleet Behavior Anomaly Detection Setup. We turn telematics and ECU data into an early warning system. For a transportation company running 600+ buses, we built the centralized telematics platform that flags abnormal fleet behavior early — the same intake architecture an anomaly-detection pipeline runs on.
- Operational Continuity Playbook. We maintain system uptime during unexpected failures. With mapped critical dependencies and verified failover paths, you run a failover, not a fire drill.
-
Vehicle SOC (VSOC) Governance & Operations
- Telemetry Intake Architecture Setup. We establish a clean data path from the vehicle to the cloud. By centralizing telemetry across domains and OTA channels, you ensure the VSOC has the complete picture needed for effective governance.
- Event Normalization & Signal Interpretation. We cut through telemetry noise to find actionable threats. By filtering high-volume data, we enable operators to tell a real indicator from a false positive — before alert fatigue sets in.
- SDV Domain Correlation Engine. Every security event arrives with its architectural context. Correlation across distributed domains reveals how an incident in one area affects others, enabling precise, impact-aware incident management.
- Real-Time Incident Playbooks. We ensure predictable, real-time remediation during complex events. Predefined recovery steps tailored to SDV platform behavior let your team run containment, not improvisation.
- VSOC Operations Dashboard. We give operators instant fleet status in one interface. A unified interface that visualizes vehicle health, domain status, and OTA channels gives leadership and operators one place to watch all of it.
-
OTA Pipeline Integrity
- End-to-End OTA Pathway Review. We determine exactly how the OTA chain performs under real-world conditions to analyze integrity and resilience.
- Update Package Integrity Validation. We create a process to verify the update structure and content before delivery to the vehicle. The team analyzes signatures, metadata, and internal package logic to ensure incorrect content never impacts ECU or SDV domain operations.
- Cloud Backend Interaction Audit. We conduct an analysis of interactions between OTA services and cloud infrastructure. We investigate backend operations and system reactions during peak loads to identify risks in update management.
- OTA Rollback Mechanism. We develop a mechanism to restore stable operation after a failed update. We define safe-mode triggers, rollback actions, and reinstallation stability so that a failed update costs a retry, not a bricked ECU.
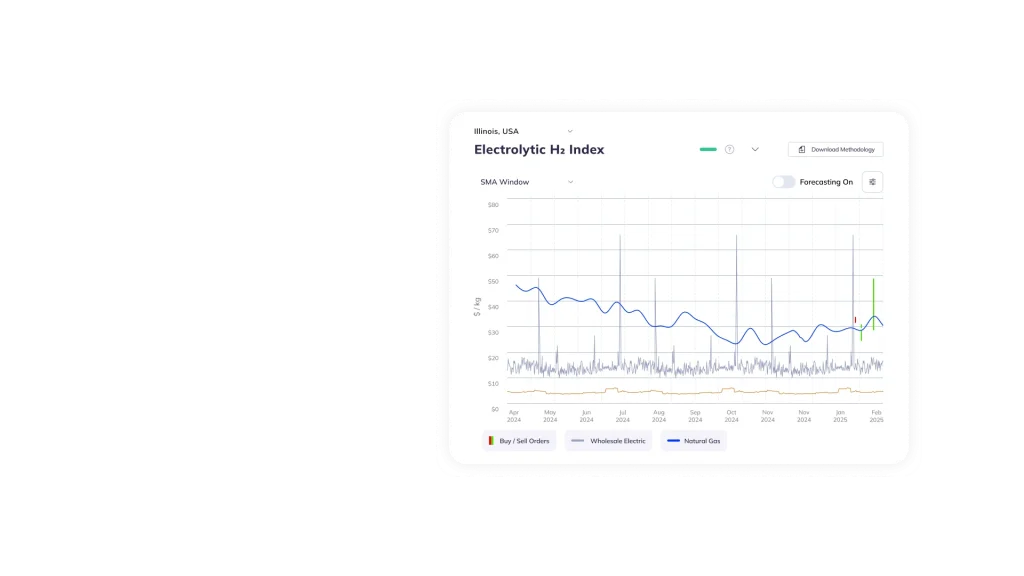

Blackcurrant: AI-Powered B2B Hydrogen Marketplace with Real-Time Carbon Tracking
An AI-powered B2B marketplace for hydrogen trading built on scalable cloud infrastructure.
Additional Info
Core Tech:
- Angular
- TypeScript
- .NET Core
- Node.js
- AWS
- NLP-powered AI engine
- Python for machine learning models
Country:
 USA
AI
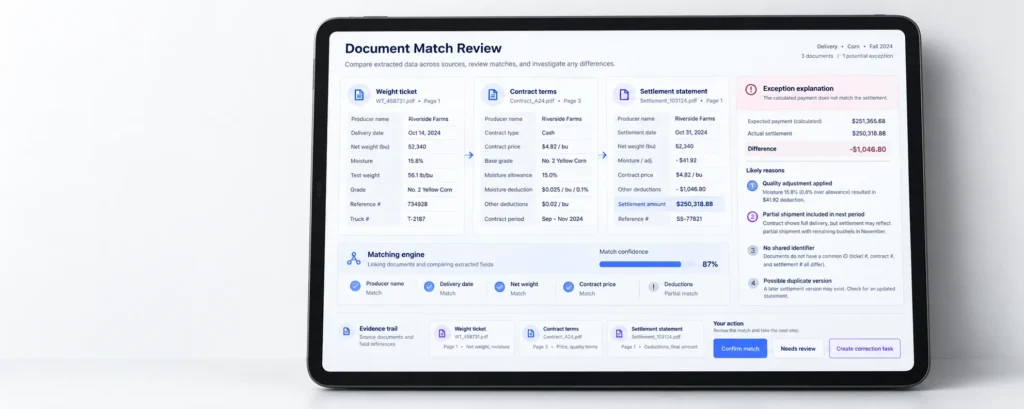
Agentic AI System for Producer Settlement Reconciliation
An agentic reconciliation layer automated matching across weight tickets, contracts, and settlement records, cut manual effort by ~70%, and kept deterministic payout calculations within the client’s existing accounting environment.
Additional Info
Core Tech:
- Python
- OpenAI
- PostgreSQL
- AWS
FINTECH
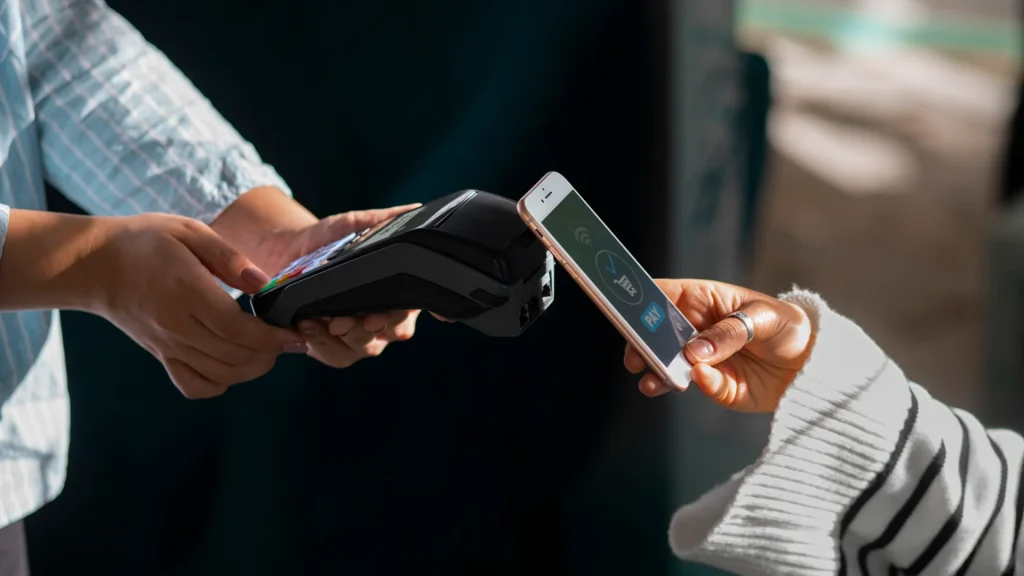
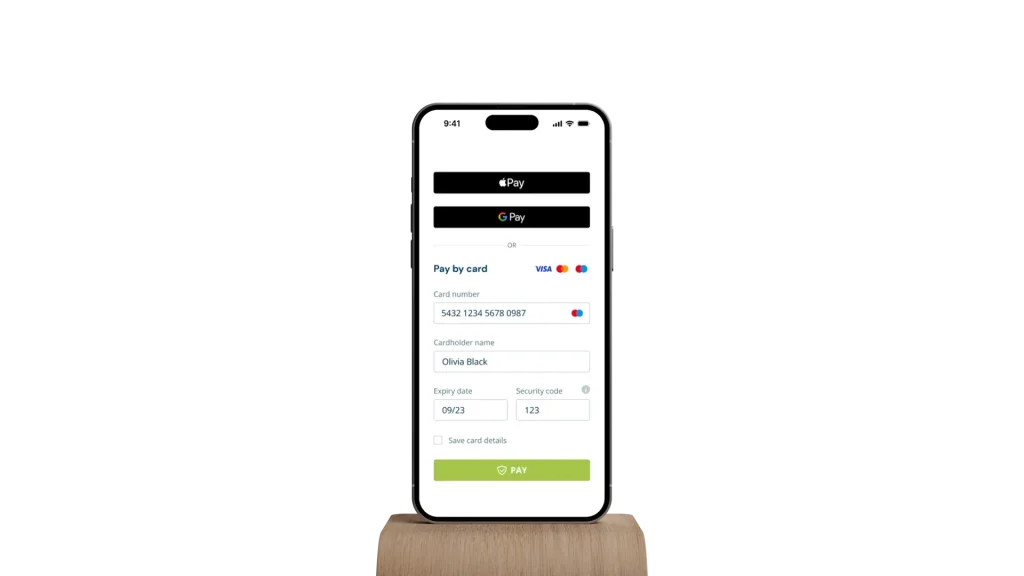
FinTech Platform for Invoicing and Secure Transactions
A fintech platform that safeguards online payments using encryption, MFA, and AI-driven fraud detection.
Additional Info
Core Tech:
- .NET microservices
- Angular 8
- PostgreSQL
- Multi-Factor Authentication (MFA)
- End-to-End Encryption
- AI-based Fraud Detection
Testimonials
Testimonials


 Sweden
The solutions they’re providing is helping our business run more smoothly. We’ve been able to make quick developments with them, meeting our product vision within the timeline we set up. Listen to them because they can give strong advice about how to build good products.
Carl-Fredrik Linné
Tech Lead at
CURE Media

 United States
We are a software startup and using Devox allowed us to get an MVP to market faster and less cost than trying to build and fund an R&D team initially. Communication was excellent with Devox. This is a top notch firm.
Darrin Lipscomb
CEO, Founder at
Ferretly


 Australia
Their level of understanding, detail, and work ethic was great. We had 2 designers, 2 developers, PM and QA specialist. I am extremely satisfied with the end deliverables. Devox Software was always on time during the process.
Daniel Bertuccio
Marketing Manager at
Eurolinx
 Australia
We get great satisfaction working with them. They help us produce a product we’re happy with as co-founders. The feedback we got from customers was really great, too. Customers get what we do and we feel like we’re really reaching our target market.
Trent Allan
CTO, Co-founder at
Active Place


 United Kingdom
I’m blown up with the level of professionalism that’s been shown, as well as the welcoming nature and the social aspects. Devox Software is really on the ball technically.
Andy Morrey
Managing Director at Magma Trading


 Switzerland
Great job! We met the deadlines and brought happiness to our customers. Communication was perfect. Quick response. No problems with anything during the project. Their experienced team and perfect communication offer the best mix of quality and rates.
Vadim Ivanenko
COO at
Optherium

 United States
The project continues to be a success. As an early-stage company, we're continuously iterating to find product success. Devox has been quick and effective at iterating alongside us. I'm happy with the team, their responsiveness, and their output.

 Sweden
We hired the Devox team for a complicated (unusual interaction) UX/UI assignment. The team managed the project well both for initial time estimates and also weekly follow-ups throughout delivery. Overall, efficient work with a nice professional team.
John Boman
Product Manager at
Lexplore


 Canada
Their intuition about the product and their willingness to try new approaches and show them to our team as alternatives to our set course were impressive. The Devox team makes it incredibly easy to work with, and their ability to manage our team and set expectations was outstanding.
Tamas Pataky
Head of Product at
Stromcore


 Estonia
Devox is a team of exepctional talent and responsible executives. All of the talent we outstaffed from the company were experts in their fields and delivered quality work. They also take full ownership to what they deliver to you. If you work with Devox you will get actual results and you can rest assured that the result will procude value.
Stan Sadokov
Product Lead at
Multilogin
 United Kingdom
The work that the team has done on our project has been nothing short of incredible – it has surpassed all expectations I had and really is something I could only have dreamt of finding. Team is hard working, dedicated, personable and passionate. I have worked with people literally all over the world both in business and as freelancer, and people from Devox Software are 1 in a million.
Mark Lamb
Technical Director at M3 Network Limited
Insights
Our Experts' Insights
AI & ML
Automotive
Fleet Management Software in 2026: 10 Capabilities Enterprises Need Beyond Telematics
AI & ML
Automotive
Legacy Modernization
Logistics
Steps from Legacy TMS to AI-Orchestrated Supply Chains
AI & ML
Automotive
Workflow Management
How to Choose a Software Partner for Automotive AI Projects: Buyer Playbook
FAQ
Frequently Asked Questions
-
How do you integrate with our SDV roadmap without impacting release velocity?
U.S. automotive teams operate in tight release cycles. We review your SDV roadmap, release windows, inter-domain dependencies, and internal delivery processes to match your operating rhythm and act as an extension of your internal team.
From there, we build a joint delivery plan that moves with your releases. Leadership can see how the work fits into the broader roadmap, while engineers receive support that reduces pressure instead of adding new blockers. We want you to focus on innovation, knowing that we have secured your foundation and kept your roadmap on track. Need the same coverage inside your own teams? That’s what our IT Staff Augmentation Services are for.
-
How do you manage complexity in zonal E/E architectures?
We start with full architectural visibility across zonal controllers, domains, and cloud services.
Then we identify critical transition points and scenarios that could affect system stability. Leadership gets a clear view of how to harden the architecture without disrupting product logic.
-
How do you ensure continuous SBOM accuracy in high-velocity CI/CD?
Our sync keeps the SBOM current on every merge, so the audit trail is built into the pipeline, not assembled before the audit. With this foundation, you move from reactive patch management to a proactive security posture, allowing your team to ship faster with absolute clarity.
-
How do you validate ADAS security against edge-case threats?
Using digital twins and signal-interference simulations, we strengthen the safety and reliability of ADAS models, keeping vehicle systems predictable and safe even against sophisticated edge-case threats. By catching these vulnerabilities before they reach the road.
-
How do you mitigate zero-day risks in legacy and modern ECUs?
We look past CVE databases for architectural defects — the ones no patch catalog lists — and harden both legacy ECUs and modern microservices against them. We don’t just defend the perimeter; we harden the core, making your platforms resilient against threats that haven’t even been discovered yet. You can also dive deeper into our AI Transformation Services.
-
How do you secure EVSE and Battery Management Systems (BMS)?
We secure the grid-vehicle interface and the BMS itself, so interference can’t degrade battery performance or take charging offline. For the complete scope, visit our automotive software engineering.
Book a call
Want to Achieve Your Goals? Book Your Call Now!
Contact Us
We Fix, Transform, and Skyrocket Your Software.
Tell us where your system needs help — we’ll show you how to move forward with clarity and speed. From architecture to launch — we’re your engineering partner.
Book your free consultation. We’ll help you move faster, and smarter.
Let's Discuss Your Project!
Share the details of your project – like scope or business challenges. Our team will carefully study them and then we’ll figure out the next move together.
Thank You for Contacting Us!
We appreciate you reaching out. Your message has been received, and a member of our team will get back to you within 24 hours.
In the meantime, feel free to follow our social.
Thank You for Subscribing!
Welcome to the Devox Software community! We're excited to have you on board. You'll now receive the latest industry insights, company news, and exclusive updates straight to your inbox.