Cybersecurity Risk Assessment Service

Let's Talk
  • KNOW WHAT MATTERS

    Know which systems hold your most valuable data.

  • SEE THE REAL RISK

    See every risk scored by likelihood and business impact.

  • ACT ON IT FAST

    Get a plan your team can start on the week the report lands.

Why It Matters

Security questions usually arrive with a deadline.

A large customer sends a security questionnaire before signing. An auditor asks for your risk register. An investor wants to see how you protect data before the next round. Each of these needs the same thing: a clear picture of where your company is exposed and what you plan to do about it.

A risk assessment gives you that picture. We look at your systems the way an attacker and an auditor would, then rank what we find by how much damage it could cause.

Modernizing unstable systems? Launching new products?

We build development environments that deliver enterprise-grade scalability, compliance-driven security, and control baked in from day one.

Check Our Portfolio
What We Offer

What the Assessment Covers

  • Exposure Management

    See your company the way an attacker sees it today and focus on the weaknesses that lead somewhere.

    • External Attack Surface Mapping
      Forgotten subdomains and old test environments are often the easiest way in. Continuous discovery tools map every internet-facing asset linked to your domains and cloud accounts. You get a full external inventory, including the systems your team lost track of.
    • Cloud and SaaS Posture Review. Cloud and SaaS settings drift with every release. CNAPP platforms such as Wiz check your cloud accounts against current benchmarks, and a separate review covers the SaaS tools your teams use daily. Your engineers get one fix list ranked by real exposure.
    • Attack Path Analysis. Individual findings tell only part of the story. Graph-based analysis links misconfigurations and excessive permissions into the routes an intruder could follow to your critical data. Fixing a single point on a path can close dozens of risks at once, and the report shows exactly where those points are.
    • Exploitability-Based Prioritization. Thousands of scanner results shrink to the few that matter. Each vulnerability is scored with EPSS and checked against the CISA catalog of known exploited vulnerabilities, then weighed against the business value of the affected asset. Your team patches what attackers actually use.
    • Validated Penetration Testing. Experienced testers try the most promising attack paths by hand. Testing follows a schedule your team approves, so production stays safe. You receive proof of what is exploitable today, which auditors and cyber insurers now ask to see.
  • Identity Risk Assessment

    Stolen credentials remain one of the most common ways into a company. This part of the assessment looks at who and what can access your systems.

    • Identity Inventory. Every person and service account with access to your systems is mapped across your identity provider and cloud platforms. Accounts left behind by former staff and old projects come to light. You get one view of who can reach what.
    • Privileged Access Review. Admin rights tend to spread over time. Access to production and finance systems is checked against each person’s current role. Your team gets a list of rights to remove and a model for granting elevated access only when a task requires it.
    • Non-Human Identities and Secrets. API keys and service accounts now outnumber human users in many cloud environments. Secret scanning across code repositories and pipelines finds credentials stored in plain text or left active for years. Each one gets an owner and a rotation plan.
    • SaaS Integrations and OAuth Grants. Connected apps often keep broad access long after anyone remembers approving them. A review of OAuth grants across your SaaS stack shows which third-party tools can read your email or files. You decide what stays connected.
    • Authentication Strength. Modern phishing kits routinely bypass push notifications and SMS codes. The review checks where phishing-resistant methods such as passkeys or hardware keys are in place and where they are missing. You get a rollout plan that starts with the accounts attackers target first.
  • AI and Supply Chain Risk

    AI tools and third-party code have become part of almost every company’s attack surface.

    • Shadow AI Discovery. Teams adopt AI assistants faster than security policies can follow. Network and SaaS logs reveal which AI services are in use and what company data flows into them. Leadership gets a clear picture to base an AI usage policy on.
    • LLM Application Testing. Chatbots and AI features in your product face new attacks such as prompt injection and data leakage. Testing follows the OWASP Top 10 for LLM Applications and MITRE ATLAS. Your product team learns which guardrails to add before an attacker or a journalist finds the gap.
    • AI Agent Permissions. AI agents that send emails or change records act with real credentials. We review each agent’s tools and permissions against the least access it needs to do its job. You get clear limits for every agent and a log trail that shows what it did.
    • Software Supply Chain. Open-source packages and build pipelines are increasingly targeted. An SBOM of your key applications lists every dependency, and pipeline checks show where malicious code could slip into a release. Your engineering team gets fixes ranked by how exposed each component is.
    • Third-Party Risk. Vendors with access to your data carry part of your risk. Critical suppliers are rated on their security posture and contract terms. You get a vendor register that supports the supply chain requirements in NIS2 and DORA.
  • Regulatory and Governance Readiness

    In the EU, regulators now hold management accountable for cyber risk, and the evidence has to be ready before anyone asks for it.

    • Regulatory Scope. European cybersecurity rules have multiplied in the last two years. Your sector and the markets you sell in decide which of them apply, from NIS2 and DORA to the EU AI Act. You get one list of obligations to plan around.
    • Framework Mapping. Existing controls are mapped to ISO 27001:2022 or NIST CSF 2.0, and to ISO 42001 if AI is central to your product. Work you have already done gets full credit. One set of controls can then serve several frameworks.
    • Gap Analysis and Evidence. Each requirement is marked by how fully you meet it today. Logs and records that prove each control works are gathered into one evidence pack during the assessment. Audits move faster, and security questionnaires from enterprise customers take far less time to answer.
    • Board Accountability. NIST CSF 2.0 made governance a core function, and NIS2 makes management responsible for cyber risk decisions. The assessment checks who owns each risk at board level and how decisions get recorded. Your directors get a governance structure they can stand behind.
    • Post-Quantum Readiness. Data encrypted today can be stolen now and decrypted once quantum computers mature. A cryptography inventory shows where vulnerable algorithms protect long-lived data. Your team gets a migration order that starts with the systems whose data must stay secret the longest.
  • Risk Quantification and Roadmap

    Every finding ends up in a form leadership can act on, and engineers can fix.

    • Financial Risk Scoring. The FAIR model turns each risk into an estimated financial loss. Leadership compares security spending in money, the unit used for every other investment. The same numbers make cyber insurance renewals easier.
    • Living Risk Register. All findings land in one register with an owner and a priority. The register loads into Jira or your GRC platform, so tracking starts the day the report arrives and stays current as fixes ship.
    • Board Briefing. A short summary covers the main risks and their likely cost, with a heat map of where exposure is concentrated. Your board gets what it needs for a decision in a few minutes of reading. Engineers receive the full findings with steps to reproduce and fix each issue.
    • Remediation Roadmap. Fixes are ordered by the risk each one removes for the effort it takes. Quick wins such as revoking stale admin accounts are flagged for the first week. Larger projects carry milestones and estimates your team can plan into sprints and budgets.
    • Continuous Reassessment. Exposure changes with every release and every new vendor. Reassessment cycles follow the CTEM model and retest the most critical attack paths. Your risk picture stays current for the next audit or board meeting.
Our Cybersecurity Risk Assessment Checklist

Our Approach

Each stage builds on the one before it. Critical issues reach you the day they are confirmed, so urgent fixes can start long before the final report.

01.

01. Agree on Scope and Goals

The kickoff call fixes the question the assessment has to answer, whether that is an audit or a large customer’s security review. Systems in scope and rules for testing are agreed in writing, and your team grants read-only access to the platforms we need. Every hour of work goes toward that goal from the first day. Result: a signed scope document with testing rules and a named contact on each side.

02.

02. Discover Assets and Identities

Discovery tools map your external attack surface and cloud accounts while our analysts pull the identity data from your identity provider. Short interviews with system owners add context that tools miss, including which AI services and vendors your teams rely on. Accounts and systems your team lost track of usually surface at this stage. Result: a complete inventory of assets and identities, each tagged by owner and business criticality.

03.

03. Test and Validate

Scans and secret detection run across the full scope, and every result is scored by how likely attackers are to exploit it. Testers then follow the most promising attack paths by hand, including your AI features where they exist. Anything critical goes to your team the same day it is confirmed. Result: a list of confirmed findings with proof of exploitability for the most serious ones.

04.

04. Quantify and Map

Each confirmed risk gets a financial estimate through the FAIR model. The same findings are mapped to the regulations and frameworks that apply to you, from NIS2 to ISO 27001:2022. Leadership sees risk in money, and your compliance lead sees exactly where the gaps are. Result: a risk register with loss estimates and a compliance gap table backed by evidence.

05.

05. Hand Over and Plan

A working session with your engineers and managers goes through every finding before the report is final. Your board receives a short briefing, and your team gets a roadmap that opens with quick wins for the first week. A date for the first reassessment is set before we close the engagement. Result: the final report, a board briefing, an evidence pack for auditors and a prioritized remediation roadmap.

  • 01. Agree on Scope and Goals

  • 02. Discover Assets and Identities

  • 03. Test and Validate

  • 04. Quantify and Map

  • 05. Hand Over and Plan

How We Can Support the Next Step

Choose the Setup That Fits Your Security Priorities

01

Discovery Sprint

We map the risk first.

We define the scope, identify critical assets, review the current environment, and turn the findings into a prioritized action plan.

Read more
02

Project-Based Delivery

We take remediation through delivery.

For a defined security scope, we own the work from planning through implementation and validation. You stay close to the key decisions while we manage execution.

Read more
03

Dedicated Team

You set the priorities. We stay on top of the risk.

For ongoing security work, we build a stable team around your roadmap. They learn your systems, controls, and risk profile, then keep improving the environment as requirements change.

Read more
04

Build-Operate-Transfer (BOT)

We build the capability. You bring it in-house.

We assemble and run the team while it establishes the processes, controls, and working knowledge your security function needs. Once the setup is proven, the team moves into your organization.

Read more
05

Staff Augmentation

You lead. We add security expertise.

Bring in experienced specialists where your team needs more depth or capacity. They work inside your existing tools, processes, and priorities while you keep full control.

Read more
Value We Provide

Benefits

01

Certified Cybersecurity Excellence

We work within frameworks such as the NIST 800 series, ISO 27K, GDPR, and others, providing in-depth assessments, vulnerability scanning, and penetration testing.

02

Industry-Specific Security Solutions

Our solutions include accurate risk identification, strategic threat analysis, and enhancement of existing security measures.

03

Trusted by the World's Leading Companies

As a trusted partner for Fortune 500 companies, Devox Software delivers proven solutions to safeguard critical operations. With a professional, consultative approach, we provide 24/7 security monitoring, endpoint resiliency strategies, and rapid responses to emerging threats.

Case Studies

Our Latest Works

View All Case Studies
Juriba Juriba
  • Backend
  • Frontend
  • Cloud
  • DevOps & Infrastructure

Juriba: Enterprise Digital Workplace Management Platform for Migration & Automation

An enterprise-grade automation platform that streamlines IT project workflows through smart dashboards.

Additional Info

Core Tech:
  • .NET 6
  • MS SQL
  • Redis
  • Angular
  • NgRx
  • RxJS
  • Kubernetes
  • Elasticsearch
Country:

United Kingdom United Kingdom

Nabed Nabed

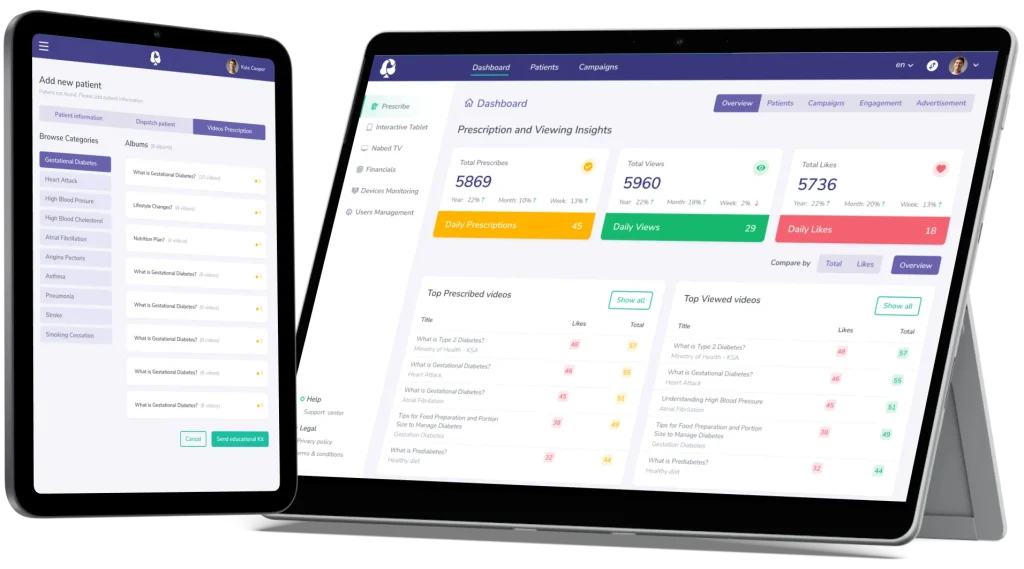
Nabed: Personalized Health Content Platform for Hospitals and Clinics

A SaaS platform bridging MedTech and MarTech to deliver personalized patient education across healthcare journeys.

Additional Info

Core Tech:
  • .NET
  • Angular
  • PostgreSQL
  • Azure
  • Docker
Country:

Lebanon Lebanon

Function4 Function4
  • website
  • management platform

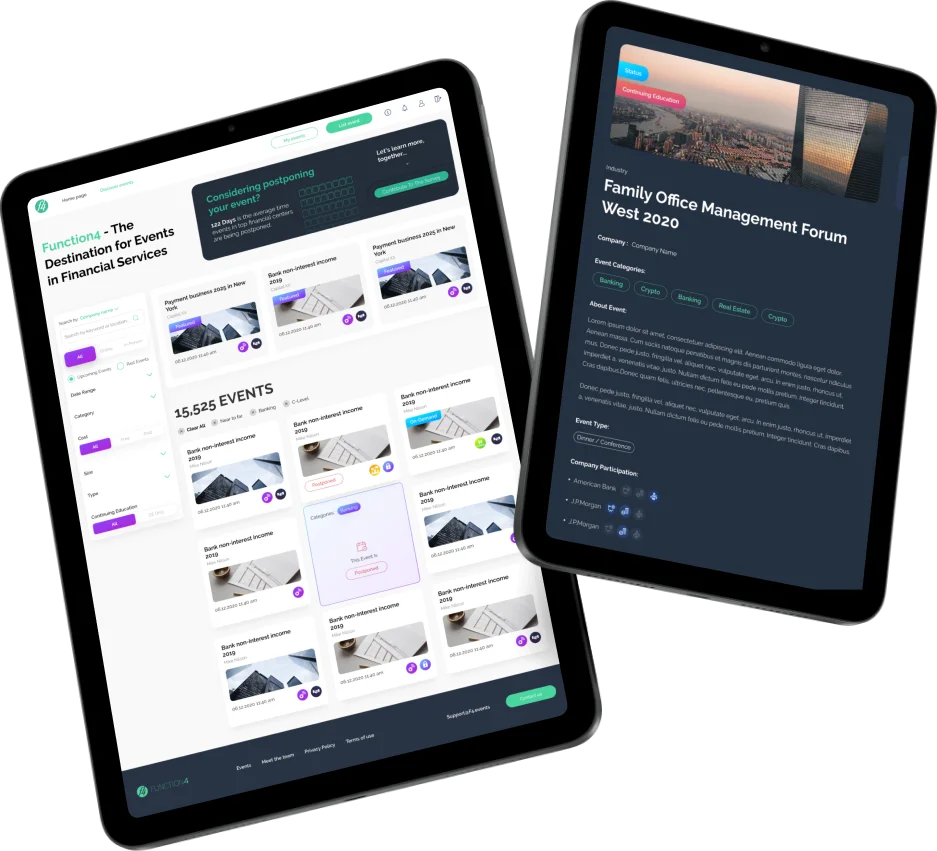
Function4: Event Management Platform for the Financial Services Industry

A feature-rich system for managing tickets, devices, invites, and communication at scale.

Additional Info

Core Tech:
  • Vue js
  • GSAP
  • Ruby
  • Azure
Country:

USA USA
Testimonials

Testimonials

Carl-Fredrik Linné                                            Sweden

The solutions they’re providing is helping our business run more smoothly. We’ve been able to make quick developments with them, meeting our product vision within the timeline we set up. Listen to them because they can give strong advice about how to build good products.

Darrin Lipscomb Darrin Lipscomb
Darrin Lipscomb United States

We are a software startup and using Devox allowed us to get an MVP to market faster and less cost than trying to build and fund an R&D team initially. Communication was excellent with Devox. This is a top notch firm.

Daniel Bertuccio Daniel Bertuccio
Daniel Bertuccio Australia

Their level of understanding, detail, and work ethic was great. We had 2 designers, 2 developers, PM and QA specialist. I am extremely satisfied with the end deliverables. Devox Software was always on time during the process.

Trent Allan Trent Allan
Trent Allan Australia

We get great satisfaction working with them. They help us produce a product we’re happy with as co-founders. The feedback we got from customers was really great, too. Customers get what we do and we feel like we’re really reaching our target market.

Andy Morrey                                            United Kingdom

I’m blown up with the level of professionalism that’s been shown, as well as the welcoming nature and the social aspects. Devox Software is really on the ball technically.

Vadim Ivanenko Vadim Ivanenko
Vadim Ivanenko Switzerland

Great job! We met the deadlines and brought happiness to our customers. Communication was perfect. Quick response. No problems with anything during the project. Their experienced team and perfect communication offer the best mix of quality and rates.

Jason Leffakis Jason Leffakis
Jason Leffakis United States

The project continues to be a success. As an early-stage company, we're continuously iterating to find product success. Devox has been quick and effective at iterating alongside us. I'm happy with the team, their responsiveness, and their output.

John Boman John Boman
John Boman Sweden

We hired the Devox team for a complicated (unusual interaction) UX/UI assignment. The team managed the project well both for initial time estimates and also weekly follow-ups throughout delivery. Overall, efficient work with a nice professional team.

Tamas Pataky Tamas Pataky
Tamas Pataky Canada

Their intuition about the product and their willingness to try new approaches and show them to our team as alternatives to our set course were impressive. The Devox team makes it incredibly easy to work with, and their ability to manage our team and set expectations was outstanding.

Stan Sadokov Stan Sadokov
Stan Sadokov Estonia

Devox is a team of exepctional talent and responsible executives. All of the talent we outstaffed from the company were experts in their fields and delivered quality work. They also take full ownership to what they deliver to you. If you work with Devox you will get actual results and you can rest assured that the result will procude value.

Mark Lamb Mark Lamb
Mark Lamb United Kingdom

The work that the team has done on our project has been nothing short of incredible – it has surpassed all expectations I had and really is something I could only have dreamt of finding. Team is hard working, dedicated, personable and passionate. I have worked with people literally all over the world both in business and as freelancer, and people from Devox Software are 1 in a million.

FAQ

Frequently Asked Questions

  • How can this risk assessment cybersecurity be applied to my company?

    Every business is unique, and so is this assessment. We tailor it to your industry, operating model, and specific needs. We assess your current security posture, uncover vulnerabilities, and provide actionable insights to protect your business from evolving cyber threats.

  • What is the ROI?

     A single security breach can cost millions in downtime, fines, and lost trust. By addressing risks upfront, you save money, protect your reputation, and boost customer confidence.

  • How long will it take?

    Most reviews are completed within 2-4 weeks. We give you a clear timeline in advance and work efficiently to minimize disruption.

  • What risks do you cover?

    From phishing attacks and compliance gaps to weak access controls and third-party vulnerabilities, we create a complete risk profile covering both internal and external threats.

  • How does this fit with our current IT or security team?

    Our external perspective brings new insights and expertise, uncovers threats your team may not see, and keeps you up to date on the latest cyber risks.

  • Is our data safe during the process?

    Absolutely. We follow strict data protection protocols and adhere to all relevant regulations.

  • Will we receive actionable recommendations?

    Yes—every identified risk comes with a customized, actionable plan.

  • Can this be integrated into our current security measures?

    Our recommendations are designed to complement your existing systems and processes and reinforce the measures you already have in place.

  • What happens after the cybersecurity risk assessment?

    We create an implementation roadmap and provide support to ensure your new security measures succeed.

  • What's special about it?

    We combine advanced tools, in-depth expertise, and a customized approach to deliver insights and strategies tailored to your specific challenges and goals.

    Take the next step: protect your business with a cybersecurity risk assessment tailored to your needs.

Book a call

Want to Achieve Your Goals? Book Your Call Now!

Having trouble booking? Open the booking page.

Contact Us

We Fix, Transform, and Skyrocket Your Software.

Tell us where your system needs help — we’ll show you how to move forward with clarity and speed. From architecture to launch — we’re your engineering partner.

Book your free consultation. We’ll help you move faster, and smarter.

Let's Discuss Your Project!

Share the details of your project – like scope or business challenges. Our team will carefully study them and then we’ll figure out the next move together.


    By sending this form I confirm that I have read and accept the Privacy Policy

    Thank You for Contacting Us!

    We appreciate you reaching out. Your message has been received, and a member of our team will get back to you within 24 hours.

    In the meantime, feel free to follow our social.


      Thank You for Subscribing!

      Welcome to the Devox Software community! We're excited to have you on board. You'll now receive the latest industry insights, company news, and exclusive updates straight to your inbox.