Vibe Coding Rescue

Let's Talk
  • RECOVER WHAT YOU SHIPPED

    Extract the core logic from AI-generated code and map every dependency to a searchable knowledge base your team maintains.

  • PROTECT WHAT MOVES MONEY

    Put financial logic, authentication, and regulated data paths behind engineering review before the next change lands.

  • SHIP THE FIXES SAFELY

    Deliver remediation slice by slice through audit-ready releases, with a named engineer approving every change before production.

Why It Matters

Why AI-Generated Code Needs Rescue

AI coding tools reset the productivity baseline across software delivery, making the move from AI prototype to production the new bottleneck.

Deploying AI-generated code reliably is where teams stall, and that gap is where vibe coding rescue work begins. Prompt-driven development earns its place in prototypes, internal tools, and demos, where speed to a first working version is the whole point. The same output moved into production lacks what the approach skipped: the standards enterprise systems require. Maintenance then turns into a rewrite, and defects surface in front of users.

Devox Software approaches AI-generated code remediation using the same governed execution model we apply to every AI-assisted engagement.

Modernizing unstable systems? Launching new products?

We build development environments that deliver enterprise-grade scalability, compliance-driven security, and control baked in from day one.

Check Our Portfolio
Our Edge

Why Choose Devox Software?

01

No documentation for the system?

We extract business logic straight from your source and map every dependency into a searchable knowledge base that stays with you for good.

02

What if we stop after the assessment?

Everything from the assessment is yours. Use it with us, another vendor, or your internal team.

03

Can AI touch our payment logic?

Protected workflows, financial logic, and regulated data paths require human approval before any change reaches them.

04

Who signs off on each fix?

Every AI-assisted change carries an audit log and a named engineer who approves it before production.

05

How do you prove a fix holds?

Deterministic validation hooks require agents to revise code and tests until the work meets defined acceptance criteria.

06

Does delivery pause during the rescue?

We release slice by slice with quality gates and rollback ready at every step, so your system keeps running throughout.

07

Can our team keep using AI tools afterward?

Yes. The harness stays: architecture and boundaries set up front, AI building within them, human-owned release gates.

08

What happens once the code is stable?

Dedicated team, staff augmentation, or managed services continue the roadmap under the same structured lifecycle described above.

What We Offer

Services We Provide

  • Vibe Coding Assessment and Code Review

    AI-assisted code reads well and passes a casual review. The gap between apparent quality and production behavior stays invisible until load, an edge case, or an audit exposes it.

    • Source-grounded system baseline. We trace dependencies and uncover hidden business logic directly from your codebase using the AI Solution Acceleratorâ„¢, then an experienced engineer reviews the findings and fills the gaps.
    • Module-level risk and security scoring. We score every module for risk and security exposure before recommending any change. Veracode reports that 45% of AI-generated code samples introduce OWASP Top 10 vulnerabilities.
    • Technical debt and architecture review. We document architectural weak points, undocumented business logic, and dependencies that make change risky, with an effort estimate for each area.
    • Security surface mapping. We map access boundaries, exposed credentials, and the paths where authorization checks are absent or applied inconsistently.
    • Committable remediation estimate. We deliver an estimate we are prepared to staff and deliver against, with the assumptions that could change it listed separately.

    We provide a clear, documented picture of your system’s reality through a detailed vibe coding audit, complete with a prioritized remediation plan and an estimate you can confidently pitch to your board or investors.

  • Living Documentation Platform

    The answers already exist, scattered across tickets, wikis, and old test cases. Reassembling them by hand consumes weeks of senior engineering time.

    • Environment-resident deployment. We build the platform within your environment, connecting source code and your comprehensive project artifacts.
    • Living documentation. The knowledge base regenerates from the source on every commit, which keeps it accurate as remediation changes the underlying system.
    • Dependency and impact map. Engineers see what each proposed change touches before they make it, which matters most in code where coupling was never designed.
    • Developer search with source references. Your team gains direct insights linked back to the exact code that produces the behavior.
    • Human-validated knowledge. Senior engineers decide what represents the product today, so outdated behavior recovered from old tickets stays out of the record.
  • Protected-Path Isolation and AI Guardrails

    Remediation carries its own risk during a vibe coding cleanup, because the parts of a system most in need of repair are frequently the parts where a mistake costs users real money.

    • Structural protection of sensitive logic. We define, by design, which paths AI is barred from touching, covering sensitive system workflows.
    • Scoped access per task. AI tools receive only the access required for a given task, with human approval mandatory for any change to a protected workflow.
    • Specs and tests before code. A senior engineer agrees on the requirement, AI generates the tests that prove it, humans review those tests, and code is validated against them.
    • Traceable authorship. Every AI-assisted change is tagged with the model used and the engineer who reviewed it, so a post-incident review has an owner for each decision.
    • Build gating. Failed builds are returned to the team and remain out of production until they pass.
  • Invariant and Regression Validation

    Test suites generated alongside the code assert whatever that code currently does. They pass even when the logic is wrong, and they lock defects in place the moment refactoring begins.

    • Invariant definition and stress testing. We define the rules your system must never break, then stress-test the code against them at scale rather than walking a checklist.
    • Side-by-side behavioral comparison. We run new logic against the previous version on identical inputs to catch silent behavior changes before release.
    • Requirements-driven test reconstruction. We rebuild coverage from your Jira tickets and codebase to target the gaps a manual QA cycle misses.
    • Release impact analysis. We show what each change affects before a single test runs, which keeps regression scope proportional to risk.
    • Coverage visibility. Your team sees tested and untested areas across the whole system before any release goes out.
  • Audit-Ready Release Engineering

    Vibe-coded systems usually reach production via an undocumented path, leaving security teams without an AI-generated code audit or evidence of what was reviewed and when.

    • Pipeline configured to your stack. We shape CI/CD around your technology and approval workflow, running automated tests and security review on every slice.
    • Automated quality gates. Every commit is validated in the pipeline as part of delivery, and unreviewed code is blocked before production.
    • Configuration drift monitoring. We watch for divergence between staging and production, so the version that passed review is the version that ships.
    • Rollback at every step. Each rollout starts small, with a rollback plan in place.
    • Audit trail with named approval. Your security and compliance teams see what was reviewed, who signed off, and when it shipped.

    This results in a release pipeline that automatically generates audit-ready evidence—exactly what your auditors and enterprise clients ask for.

  • Governed Delivery After the Rescue

    Remediation without a change in the operating model yields the same findings within two quarters, because the delivery pressure and the tooling stay exactly as they were.

    • Architecture and boundaries set upfront. Senior engineers define the structure AI operates within before any generation occurs.
    • AI-assisted implementation under review. Features land faster while senior engineers own integration logic and edge cases.
    • AI-assisted code review with human sign-off. Security exposure and long-term technical debt stay a senior engineering decision.
    • Living documentation maintained from source. Documentation updates on every commit and stays connected to tickets and test cases.


Our Process

The Vibe Coding Rescue Lifecycle

01.

01. Day 0: Repo Audit

This phase runs the same assessment as our standalone Vibe Coding Audit (completed in 3-5 business days). We establish how the system works today, tracing dependencies and recovering business logic from source. An experienced engineer reviews the findings and identifies the riskiest areas to change.

02.

02. Week 1: Triage and Stop-the-Bleeding Fixes

We turn the baseline into a plan broken into small, testable releases. High-risk changes, such as billing and authentication, are moved later in the sequence, so your product owner can approve the plan without reviewing code.

03.

03. Weeks 2-6: Hardening and Stabilization

We implement production-grade security, including Row-Level Security (RLS) and secrets management, establish automated integration tests, and configure safe, staged deployment pipelines. We validate every module for data integrity under load.

04.

04. Weeks 7-8: Migration, Launch, and Handover

We manage the production cutover and final data migration, conduct a 60-minute system walkthrough for your team, and provide the final hand-off with all documentation, CI pipelines, and Guardrails.

  • 01. Day 0: Repo Audit

  • 02. Week 1: Triage and Stop-the-Bleeding Fixes

  • 03. Weeks 2-6: Hardening and Stabilization

  • 04. Weeks 7-8: Migration, Launch, and Handover

Benefits

Why Engineering Leaders Choose Devox for AI Code Remediation

  • The Harness Comes With the Rescue

    Most rescue offers end when the code stabilizes, leaving the original failure conditions intact. Devox Software integrates the AI Solution Acceleratorâ„¢ directly into your environment as a permanent harness. It features: grounded context so analysis works from your actual source; scoped permissions that keep AI away from protected workflows; deterministic validation that ensures work meets acceptance criteria; and an audit trail for every change. This maintains long-term governance long after the initial remediation is complete.

  • Knowledge and Artifacts That Stay With You

    All deliverables from the assessment and remediation belong to your company. These include the system baseline, dependency map, risk scoring, reconstructed test suites, CI/CD pipelines, and a Living Documentation Platform. We deploy this platform directly inside your environment by extracting business logic from your source code, ensuring it updates automatically on every commit so that critical system knowledge remains fully accessible long after the project ends.

  • Accountability at Every Gate

    Devox Software delivers into environments where defects carry significant legal and financial consequences, including high-stakes, regulated industries. Each AI-assisted change has an audit log and a named engineer behind it, and each release records what was reviewed and who approved it. Every engineer on your project works for us, so departures and absences stay our problem rather than yours.

Industry Standards & Frameworks

Relevant Industry Standards & Controls

Your compliance and security goals guide our process. We design our workflows to help you maintain adherence to these industry frameworks, documenting every decision and approval from initial assessment through release.

[Security & Data-Privacy Standards]

  • ISO/IEC 27001

  • SOC 2

  • GDPR

  • CCPA/CPRA

  • OWASP Top 10 for LLM & Agentic Applications

[Cloud & Infrastructure Compliance]

  • Azure Well-Architected Framework

  • AWS Well-Architected Framework

  • NIST CSF

  • CIS Benchmarks

[AI Governance & Accountability]

  • ISO/IEC 42001 (AI Management System)

  • NIST AI RMF 1.0 (+ Generative AI Profile)

  • EU AI Act

  • Policy-as-Code controls

  • Continuous Compliance Pipelines

[Responsible AI & Human Oversight]

  • OECD AI Principles

  • Human-in-the-loop controls

  • Model cards & system documentation

  • Adversarial testing & red-teaming

Case Studies

Our Latest Works

View All Case Studies
AI Dependency Mapping in Action: Cutting Modernization Costs for a Fintech Platform by 30% AI Dependency Mapping in Action: Cutting Modernization Costs for a Fintech Platform by 30%

AI Dependency Mapping in Action: Cutting Modernization Costs for a Fintech Platform by 30%

An AI-driven fintech modernization that mapped 450k lines of dependencies, cut costs by 30%, and enabled zero-downtime migration to Azure.

Additional Info

Core Tech:
  • .NET Framework
  • .NET 8
  • C#
  • SQL Server
  • Azure Functions
  • Azure App Services
  • micro-frontends
  • Terraform
  • GitHub Actions
  • SonarQube
Country:

USA USA

ActivePlace ActivePlace
  • health
  • fitness
  • marketplace

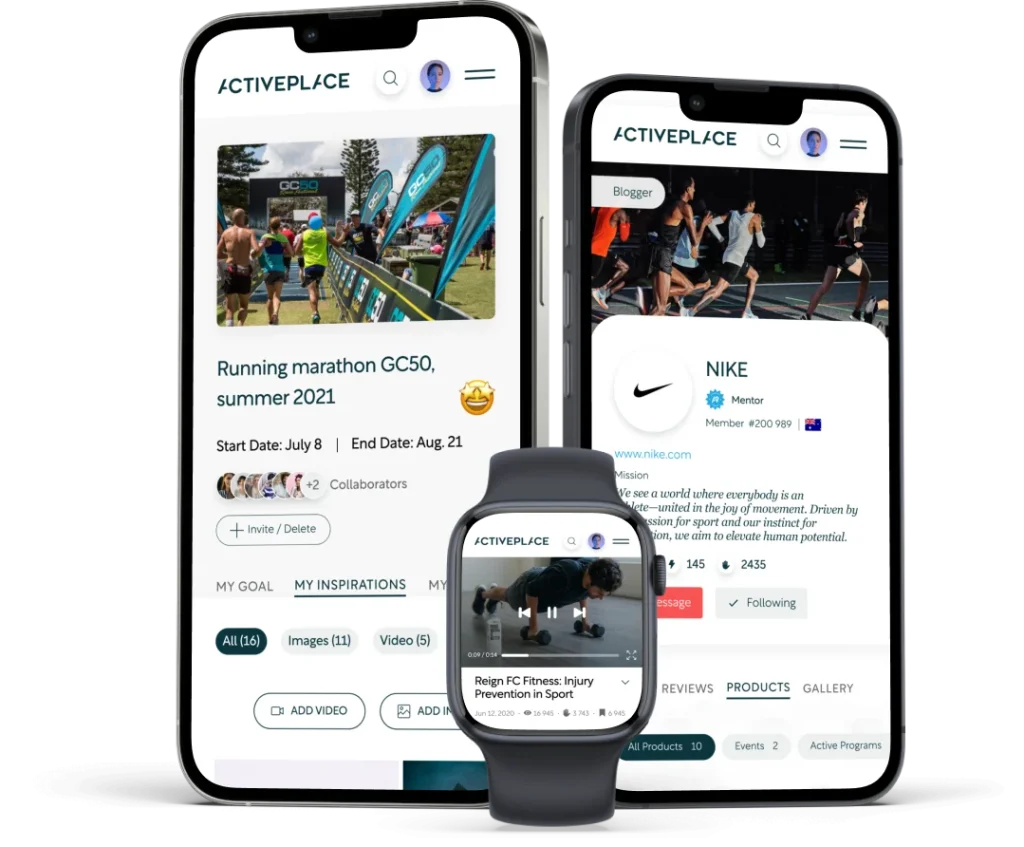
ActivePlace: Wellness-Focused Social Marketplace Platform

A wellness-focused social media and marketplace platform for active lifestyle communities.

Additional Info

Core Tech:
  • Jenkins
  • Angular
  • Ruby
  • Figma
Country:

Australia Australia

Humanising Autonomy: Behavioral AI SDK for Humanized Driver Assistance Systems (HDAS) Humanising Autonomy: Behavioral AI SDK for Humanized Driver Assistance Systems (HDAS)
  • AUTONOMOUS DRIVING
  • C++ DEVELOPMENT
  • COMPUTER VISION
  • AI OPTIMIZATION
  • ETHICAL AI

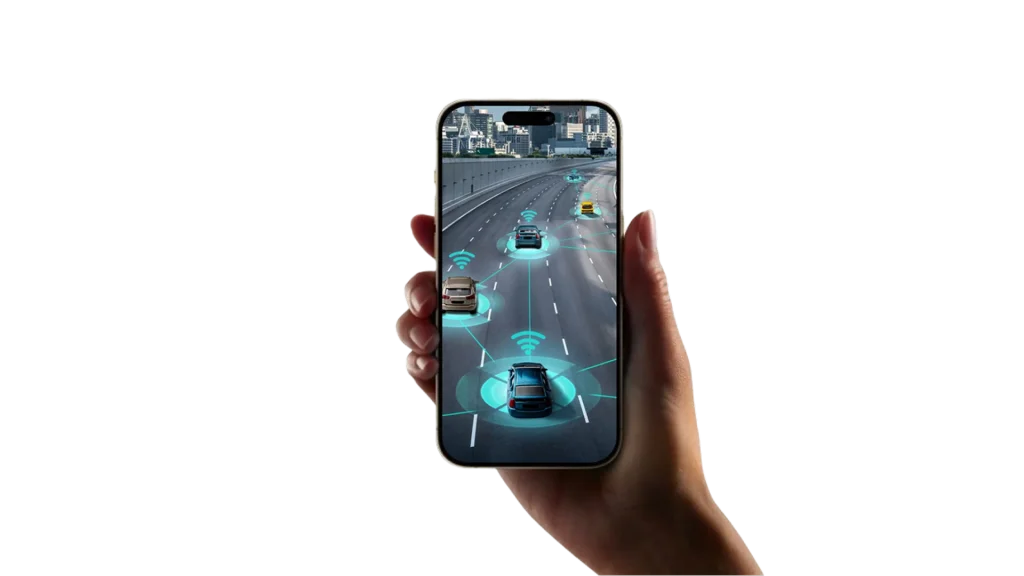
Humanising Autonomy: Behavioral AI SDK for Humanized Driver Assistance Systems (HDAS)

A computer vision SDK for predicting road user behavior and enhancing driver safety.

Additional Info

Core Tech:
  • C++
  • OpenCV
  • CUDA
  • Github Actions
  • Cmake
  • Conan
  • TensorRT
  • ONNX
  • Ambarella
Country:

United Kingdom United Kingdom
Testimonials

Testimonials

Carl-Fredrik Linné                                            Sweden

The solutions they’re providing is helping our business run more smoothly. We’ve been able to make quick developments with them, meeting our product vision within the timeline we set up. Listen to them because they can give strong advice about how to build good products.

Darrin Lipscomb Darrin Lipscomb
Darrin Lipscomb United States

We are a software startup and using Devox allowed us to get an MVP to market faster and less cost than trying to build and fund an R&D team initially. Communication was excellent with Devox. This is a top notch firm.

Daniel Bertuccio Daniel Bertuccio
Daniel Bertuccio Australia

Their level of understanding, detail, and work ethic was great. We had 2 designers, 2 developers, PM and QA specialist. I am extremely satisfied with the end deliverables. Devox Software was always on time during the process.

Trent Allan Trent Allan
Trent Allan Australia

We get great satisfaction working with them. They help us produce a product we’re happy with as co-founders. The feedback we got from customers was really great, too. Customers get what we do and we feel like we’re really reaching our target market.

Andy Morrey                                            United Kingdom

I’m blown up with the level of professionalism that’s been shown, as well as the welcoming nature and the social aspects. Devox Software is really on the ball technically.

Vadim Ivanenko Vadim Ivanenko
Vadim Ivanenko Switzerland

Great job! We met the deadlines and brought happiness to our customers. Communication was perfect. Quick response. No problems with anything during the project. Their experienced team and perfect communication offer the best mix of quality and rates.

Jason Leffakis Jason Leffakis
Jason Leffakis United States

The project continues to be a success. As an early-stage company, we're continuously iterating to find product success. Devox has been quick and effective at iterating alongside us. I'm happy with the team, their responsiveness, and their output.

John Boman John Boman
John Boman Sweden

We hired the Devox team for a complicated (unusual interaction) UX/UI assignment. The team managed the project well both for initial time estimates and also weekly follow-ups throughout delivery. Overall, efficient work with a nice professional team.

Tamas Pataky Tamas Pataky
Tamas Pataky Canada

Their intuition about the product and their willingness to try new approaches and show them to our team as alternatives to our set course were impressive. The Devox team makes it incredibly easy to work with, and their ability to manage our team and set expectations was outstanding.

Stan Sadokov Stan Sadokov
Stan Sadokov Estonia

Devox is a team of exepctional talent and responsible executives. All of the talent we outstaffed from the company were experts in their fields and delivered quality work. They also take full ownership to what they deliver to you. If you work with Devox you will get actual results and you can rest assured that the result will procude value.

Mark Lamb Mark Lamb
Mark Lamb United Kingdom

The work that the team has done on our project has been nothing short of incredible – it has surpassed all expectations I had and really is something I could only have dreamt of finding. Team is hard working, dedicated, personable and passionate. I have worked with people literally all over the world both in business and as freelancer, and people from Devox Software are 1 in a million.
Insights

Our Experts' Insights

Revolutionizing Farming Practices with AI Technology

Scaling Trust: How AI-Augmented Architectures Accelerate Web3 Business Adoption

Voice & Speech Recognition Solutions for Your Product. Does It Pay off?

FAQ

Frequently Asked Questions

  • Should we rewrite the AI-generated application or repair it?

    Three factors decide it: how much of the business logic is correct and worth preserving, how deep the architectural problems reach into the data model, and how much the product is expected to change over the next eighteen months. An application with sound domain logic and a defensible schema, wrapped in messy but isolated implementation, is a repair candidate. An application whose data model encodes contradictory assumptions usually costs more to fix than to rebuild around a preserved specification.

    Devox Software resolves this during the assessment rather than through opinion. We score risk and security across every module before recommending a change, and each module receives a verdict with the reasoning and the effort attached. Most engagements yield a mixed result: the majority of the system is repaired in place, while a small number of components are rebuilt. The documented reasoning stays with you, making the decision defensible to your board or investors.
  • How do you assess a codebase when there is no reliable documentation?

    Missing documentation is the normal starting condition for vibe coding rescue, and comments generated alongside the code often describe intent the implementation never fulfilled. Working from those artifacts produces a confident and wrong picture. Devox Software establishes ground truth from the system itself: we build a knowledge graph of the codebase from language-server data, trace dependencies and data flow across components, and recover business logic from source. Senior engineers then review the output and fill the gaps left by machine analysis.

    Years of product logic scattered across tickets, wikis, and old test cases can be summarized and cross-referenced at scale, which compresses weeks of manual archaeology. Deciding which of it still represents the product stays a senior engineering call. That evidence base becomes the Living Documentation Platform your team works from afterward, updated from source on every commit.

  • How do you keep AI away from the parts of the system that hold money or regulated data?

    Structurally, before any work starts, protected workflows, financial logic, authentication, and regulated data paths are defined as off-limits inside the harness, regardless of how a task is framed. In a typical crypto wallet engagement, for example, that boundary covers keys, signing, recovery, and money movement, while AI works freely on scaffolding, internal tools, UI, parsers, and tests. The split is a design decision made with your engineers, recorded, and enforced by permissions.

    Everything crossing a protected boundary requires human approval, and every AI-assisted change anywhere in the system is logged, naming the model used and the engineer who reviewed it. Deterministic validation hooks hold work until it meets defined acceptance criteria before it can progress, and failed builds stay out of production. This is what makes AI-generated code acceptable in environments subject to SOC 2, GDPR, or the EU AI Act: the controls and evidence, rather than the origin of any individual line.

  • Can our team keep using AI coding tools after the engagement?

    Yes, and stopping IDE assistants or environments like Replit would usually be the wrong trade. The velocity these tools deliver is real, and the problems come from the absence of a control layer around them. The AI Solution Acceleratorâ„¢ harness serves as a permanent, human-owned control layer that preserves high development velocity while keeping your codebase secure and consistent.

    We also address the human side, since guardrails only hold when the team understands them. Handover covers where AI assistance, including workflows from v0, works well in your specific codebase, which categories of change require senior review, and how to read the generated output to identify the failure modes that surfaced during the rescue. Teams that complete this step maintain their delivery pace while their defect and security findings drop because the tooling operates within the boundaries the team helped set.

  • How much does a vibe coding rescue cost?

    Cost is determined by the codebase size and risk profile, and is scoped after the initial fixed-price audit.

  • How long does a typical rescue take?

    A typical rescue engagement takes 8 weeks, with immediate triage in Week 1.

  • What if my project is in production and I can't afford downtime?

    We release slice by slice, with a rollback path prepared for each one and staging isolated from production, ensuring your system remains fully operational throughout.

  • Is this a penetration test or compliance certification?

    No, this is a code remediation and structural security review, though we align with OWASP and SOC 2 guidelines.

  • Can't our first hire clean it up?

    First hires spend months on technical archaeology before they can safely change anything, and a freelance developer lacks the senior governance, structured QA, and security analysis needed to stabilize a complex AI-built codebase. The audit hands your team the dependency map and risk scoring on day one, accelerating onboarding and ensuring immediate standards.

Book a call

Want to Achieve Your Goals? Book Your Call Now!

Contact Us

We Fix, Transform, and Skyrocket Your Software.

Tell us where your system needs help — we’ll show you how to move forward with clarity and speed. From architecture to launch — we’re your engineering partner.

Book your free consultation. We’ll help you move faster, and smarter.

Let's Discuss Your Project!

Share the details of your project – like scope or business challenges. Our team will carefully study them and then we’ll figure out the next move together.


    By sending this form I confirm that I have read and accept the Privacy Policy

    Thank You for Contacting Us!

    We appreciate you reaching out. Your message has been received, and a member of our team will get back to you within 24 hours.

    In the meantime, feel free to follow our social.


      Thank You for Subscribing!

      Welcome to the Devox Software community! We're excited to have you on board. You'll now receive the latest industry insights, company news, and exclusive updates straight to your inbox.