Virtual Chief Information Security Officer (vCISO) as a Service

Virtual Chief Information Security Officer (vCISO) as a Service

Protect what matters most from cyber threats with with Devox Software's vCISO as a Service proactive security measures and expert leadership. Stay ahead of evolving risks and defend sensitive data, knowing your defenses are in the hands of professionals.

Book a call
Why Businessess Choose vCISO Services?

When Do You Need vCISO to Fill In?

01

To Recover from Breaches Fast

A data breach can cripple user trust and tarnish your brand. Devox Software's expertise takes charge, developing a detailed incident response plan, securing your systems and restoring confidence in your product’s safety and reliability.

02

To Build Resilience for Threats

Zero-day exploits, advanced persistent threats, and supply chain attacks are real. Devox Software’s vCISO service anticipates these risks, deploying multi-layered protections that make your product resilient against even the most sophisticated attacks so you will never get a panicking 2 am wake-up call.

03

To Make Compliance Checks Easy

Compliance buys peace in many ways: no watchdogs up your head, meeting standards of GDPR, HIPAA, or PCI-DSS by design, calmness around protection level and a rock-solid confidence when selling the business. Our vCISO will bring clear, actionable strategies tailored to your product’s unique regulatory background so it doesn’t feel like an endless maze, with severe consequences for missteps.

04

To Eliminate Budget Constraints

Hiring a full-time CISO or building an in-house team may be out of reach, but the risks of neglecting security are far greater. Devox Software’s vCISO offers enterprise-grade expertise without the overhead, delivering value and results that align with your budget and goals.

05

To Ensure Safe Upscaling

Rapid growth often exposes gaps in security, making your product an attractive target for cybercriminals. Devox Software ensures your defenses scale alongside your user base and infrastructure, preventing vulnerabilities that could derail your progress.

06

To Reinforce Leadership

As a CEO or CTO, your focus is divided between innovation, delivery, and managing risk. Devox Software takes security off your plate, embedding it into your product lifecycle so you can prioritize growth without compromise. Our vCISO steps in to provide clarity, aligning security with your product roadmap while easing the burden on your shoulders.

What vCISO Functions You Get

vCISO Services We Offer

A virtual Chief Information Security Officer (vCISO) is an external cybersecurity leader who provides part-time, fractional, or interim CISO-level guidance without joining the company as a full-time executive. A vCISO typically helps set security strategy, prioritize risk, guide compliance efforts, coordinate security initiatives, advise leadership, and track the organization’s overall security posture. We offer a range of vCISO services that will help you keep safe and dodge the hacker bullet.

  • Cybersecurity Strategy Development

    Get a business-aligned cybersecurity strategy designed and implemented according to your unique goals and risk profile. Devox Software’s vCISO experts ensure that every layer of your security measures integrates seamlessly with your operations, positioning you to tackle current and emerging threats effectively. What you get with vCISO cybersecurity strategy development :

    • Risk assessment to identify vulnerabilities and prioritize threats
    • Setting clear security objectives aligned with business goals
    • Designing enforceable security policies and frameworks
    • Ensuring compliance with regulations like GDPR, HIPAA, and ISO 27001
    • Evaluating and recommending technologies to enhance security
    • Developing a detailed incident response plan
    • Integrating security into business processes, IT workflows, and product development
    • Regular evaluations and updates to keep the strategy effective
    Read more
  • Risk Assessment and Maturity Roadmapping

    Evaluate your current security posture across governance, technology, processes, people, third-party risk, and regulatory requirements to identify the gaps that matter most. The vCISO by Devox Software helps distinguish urgent exposures from lower-priority issues, assess how mature existing controls are, and connect technical findings to business impact.

    The result is a practical security roadmap with prioritized initiatives, ownership, sequencing, and measurable milestones. Instead of treating every weakness as equally urgent, the roadmap helps leadership focus budget and effort on the changes that reduce meaningful risk and support the organization’s growth, compliance, and operational goals.

    Read more
  • Data Privacy/DPO-Adjacent Support

    Support the security side of data privacy by helping map sensitive data, review access controls, assess data-handling risks, and align security practices with relevant privacy requirements. A vCISO works with legal, compliance, IT, and engineering teams to translate privacy obligations into practical technical and organizational controls.

    We support privacy-impact reviews, data-retention practices, incident coordination, vendor risk, and evidence preparation. The goal is to strengthen privacy governance from a cybersecurity perspective while keeping formal legal interpretation and statutory DPO responsibilities with appropriately qualified legal or privacy professionals where required.

  • Artificial Intelligence in Cybersecurity

    Use AI to strengthen security operations where large volumes of alerts, logs, user activity, and system behavior make manual analysis difficult to scale. AI-supported security workflows surface anomalies, prioritize suspicious activity, correlate signals across systems, and give security teams more context for investigation and response.

    A vCISO from Devox Software evaluates where AI adds practical value, defines appropriate use cases, assesses data and integration requirements, and establishes governance around how AI-driven security tools are deployed. The focus always remains on improving detection and decision support while keeping human oversight, access controls, and risk management in place.

    Read more
  • Cyber Insurance Readiness Advisory

    Prepare your organization for cyber insurance applications, renewals, and underwriter reviews by assessing whether current security controls, documentation, and risk-management practices align with common insurer expectations. A vCISO identifies gaps around identity and access management, backups, incident response, endpoint protection, vulnerability management, vendor risk, and other areas that may influence underwriting decisions.

    Devox Software’s vCISO scope also supports evidence gathering, remediation prioritization, and coordination with internal teams before questionnaires or insurer reviews are completed. The goal is to improve readiness and reduce avoidable friction during the insurance process without implying guaranteed coverage, premiums, or underwriting outcomes.

  • Compliance and Gap Analysis

    Assess your current security controls, policies, processes, and documentation against the requirements that matter to your business, such as ISO 27001, SOC 2, HIPAA, PCI DSS, GDPR, or customer security expectations. The vCISO identifies where existing practices fall short, separates documentation gaps from technical control gaps, and helps prioritize the work needed to improve readiness.

    As a result, you get a clear remediation plan that maps each gap to an owner, required action, and business priority. This gives leadership a practical path toward stronger audit readiness and compliance alignment without treating every requirement as equally urgent.

  • Security Policies and Training by vCISO

    Develop and maintain security policies that reflect how your organization actually operates, including access control, data handling, incident response, acceptable use, vendor security, remote work, and other relevant areas. The vCISO translates security and compliance requirements into practical rules, ownership, and review cycles that teams can follow.

    The vCISO service by Devox Software supports role-based security awareness and training programs for employees, managers, and technical teams. The goal is to reduce policy gaps, clarify individual responsibilities, and make security expectations part of day-to-day operations rather than a set of documents reviewed only during audits.

  • Security Architecture Review and and Threat Monitoring

    Establish a clear incident response framework so teams know how to detect, escalate, contain, investigate, and recover from security events. The vCISO helps define response roles, communication paths, decision criteria, playbooks, and executive reporting so incidents are handled through a coordinated process rather than improvised under pressure.

    You also get an oversight of threat-monitoring practices, alerting workflows, and escalation thresholds across relevant security tools and teams. The goal is to improve visibility, reduce response delays, and give leadership a clearer view of active risks, recurring threats, and the actions required to strengthen defenses over time.

    Devox  Software ensures your security infrastructure is resilient by combining third-party risk assessments with comprehensive architecture reviews. We assess the security arrangements of your partners and vendors and ensure that they meet your standards and don’t compromise your systems. At the same time, our vCISO experts analyze your internal security architecture, identify gaps, and optimize them to support your goals.

    Read more
  • Interim or Fractional Security Leadership

    Provide experienced security leadership during periods when a full-time CISO is unavailable, unnecessary, or still being hired. A vCISO steps in to set priorities, coordinate security initiatives, guide risk and compliance decisions, support executive stakeholders, and keep critical programs moving without leaving ownership fragmented.

    We structure our work around ongoing fractional leadership or a defined interim period, depending on the organization’s needs. This gives the business senior-level security direction while maintaining flexibility around scope, time commitment, and long-term hiring plans.

  • M&A and Fundraising Security Due Diligence

    Assess cybersecurity risks that could affect a transaction, investment, or fundraising process, including control gaps, unresolved vulnerabilities, compliance exposure, third-party dependencies, incident history, and weaknesses in security governance. A vCISO organizes technical findings into a clear risk view for executives, investors, buyers, or other stakeholders.

    We support remediation planning before diligence begins, help prepare security documentation and evidence, and identify issues that may require disclosure or executive attention. The goal is to reduce surprises during diligence and give decision-makers a clearer understanding of the security risks attached to the business.

  • Security Budget Planning and Tool Stack Rationalization

    Align cybersecurity spending with the risks, business priorities, and compliance requirements that matter most. A vCISO builds a practical security budget, prioritizes investments, and separates essential controls from lower-value initiatives so leadership has a clearer basis for funding decisions.

    We also review the existing security tool stack to identify overlap, unused capabilities, integration gaps, and unnecessary spend. The goal is to simplify the environment where possible, improve coverage, and make sure security investments support a coherent program rather than a collection of disconnected tools.

Benefits of Devox Software-based vCISO

Why Choose Devox Software

  • Fraction of Full-Time CISO Cost

    Get access to senior cybersecurity leadership without carrying the full compensation, benefits, recruiting, and long-term overhead of a permanent CISO hire.

  • Access to Senior Talent

    Bring experienced security leadership into the business without waiting through a lengthy executive hiring process. A vCISO can provide senior-level guidance on risk, compliance, security strategy, incident readiness, architecture decisions, and executive communication from the start of the engagement

  • Scalable, Flexible Terms

    Adjust the level of vCISO support as your security needs change. Engagements can scale from periodic advisory and executive reporting to more embedded fractional leadership during audits, major remediation programs, rapid growth, or leadership transitions.

  • Team-Backed Delivery

    Get more than one person’s perspective or availability. A team-backed vCISO model can combine executive security leadership with access to specialists across areas such as cloud security, application security, compliance, risk, penetration testing, and incident response when the engagement requires deeper technical input.

  • Named Framework Expertise

    Apply recognized security and compliance frameworks to structure risk decisions, control priorities, and program maturity. A vCISO maps current practices against frameworks such as NIST Cybersecurity Framework, ISO 27001, CIS Controls, SOC 2 criteria, HIPAA, PCI DSS, or GDPR requirements.

How We Work

Our vCISO Setup and Working Process

01.

01. Initial Assessment and Onboarding (1–2 weeks)

  • Reviewing your existing infrastructure, policies, and processes.
  • Identifying potential vulnerabilities, risks, and compliance gaps.
  • Aligning security goals with your business and product objectives.
  • Receiving a comprehensive report detailing your current state, risks, and recommended immediate actions.
02.

02. Strategy Development (2–4 weeks)

  • Crafting a security roadmap aligned with your growth trajectory.
  • Prioritizing actions based on risk severity and business impact.
  • Defining KPIs to measure the success of the implemented measures.
  • Developing data protection, access control, and incident response policies.
  • Implementing secure coding practices if applicable.
  • Conducting training sessions to align your team with the new protocols.
03.

03. Threat Monitoring and Incident Response Planning (2–6 weeks for setup)

  • Implementing advanced monitoring tools to detect potential breaches in real time.
  • Conducting regular vulnerability scans and penetration testing.
  • Updating security measures based on emerging threats and trends.
  • Developing a robust incident response plan tailored to your product.
  • Conducting tabletop exercises to prepare your team for potential breaches.
  • Leading incident response efforts if a breach occurs, from containment to recovery.
  • Deliver a tested and ready-to-deploy incident response plan.
04.

04. Compliance and Certification Support (4–12+ weeks)

  • Aligning your security practices with standards such as GDPR, HIPAA, ISO 27001, or PCI-DSS.
  • Providing documentation and guidance for audits or certifications.
  • Addressing any compliance gaps to avoid penalties or legal risks.
  • Deliver audit-ready documentation and compliance certifications.
05.

05. Executive Reporting and Ongoing Advisory (ongoing)

  • Providing regular updates and reports to the leadership team.
  • Advising on security implications of business decisions, such as new market entries or product launches.
  • Reassessing and evolving the security strategy as your business grows.
  • Delivering monthly or quarterly executive reports and strategic advisory sessions.
06.

06. Transition and Knowledge Handoff (1–3 weeks)

  • Training your internal team to sustain and evolve the security framework.
  • Documenting all implemented processes, tools, and strategies for future reference.
  • Remaining available for ongoing advisory or support if needed.
  • Delivering a fully documented and operationalized security framework ready for use.
  • 01. Initial Assessment and Onboarding (1–2 weeks)

  • 02. Strategy Development (2–4 weeks)

  • 03. Threat Monitoring and Incident Response Planning (2–6 weeks for setup)

  • 04. Compliance and Certification Support (4–12+ weeks)

  • 05. Executive Reporting and Ongoing Advisory (ongoing)

  • 06. Transition and Knowledge Handoff (1–3 weeks)

Case Studies

Our Latest Works

View All Case Studies
Trading System for Confidential Market Execution Trading System for Confidential Market Execution
  • Fintech
  • ATS

Trading System for Confidential Market Execution

A fintech trading system enabling anonymous, low-impact transactions between institutional players.

Additional Info

Core Tech:
  • .NET Core
  • Kafka
  • Redis
  • React.js
  • WebSockets
  • OAuth 2.0
  • PostgreSQL
  • Selenium
Country:

USA USA

Nabed Nabed

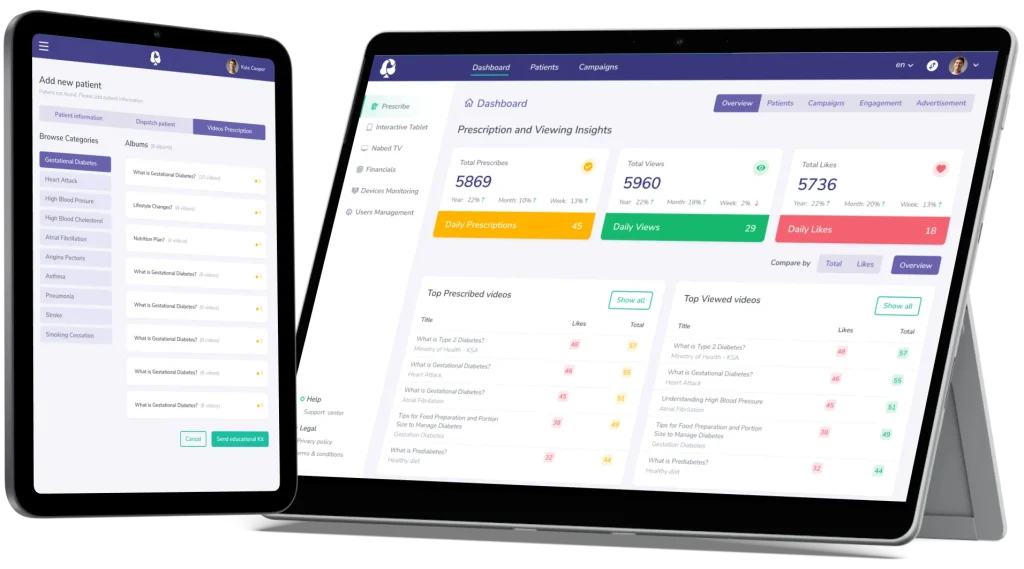
Nabed: Personalized Health Content Platform for Hospitals and Clinics

A SaaS platform bridging MedTech and MarTech to deliver personalized patient education across healthcare journeys.

Additional Info

Core Tech:
  • .NET
  • Angular
  • PostgreSQL
  • Azure
  • Docker
Country:

Lebanon Lebanon

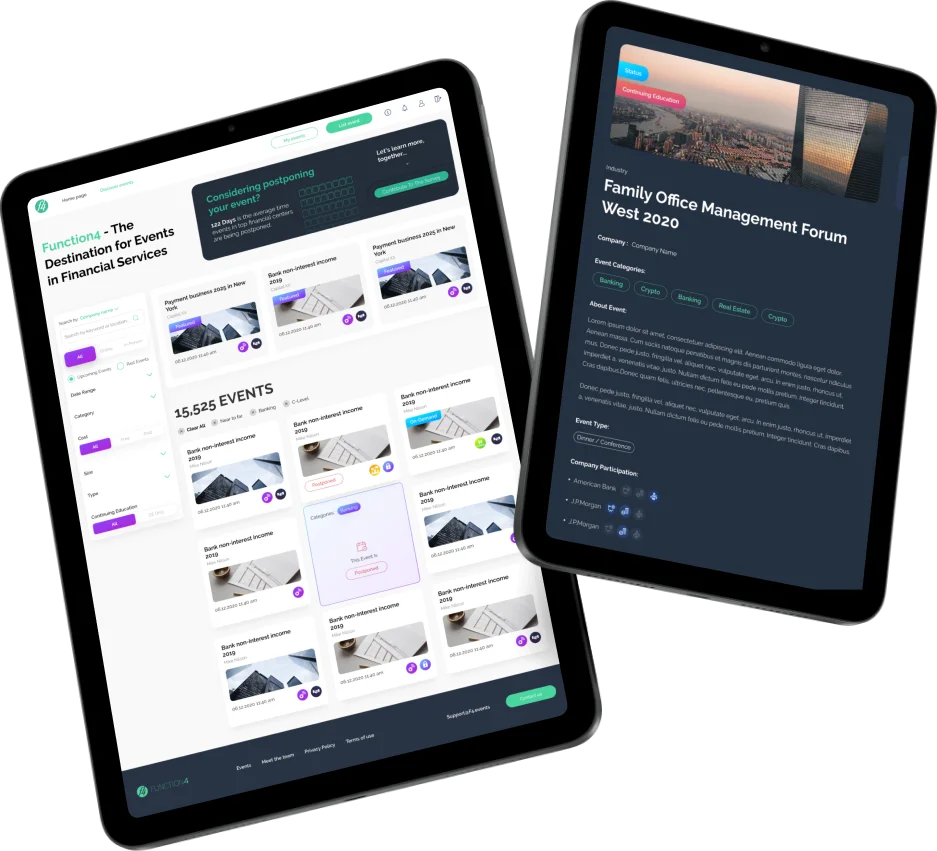
Function4 Function4
  • website
  • management platform

Function4: Event Management Platform for the Financial Services Industry

A feature-rich system for managing tickets, devices, invites, and communication at scale.

Additional Info

Core Tech:
  • Vue js
  • GSAP
  • Ruby
  • Azure
Country:

USA USA

Juriba Juriba
  • Backend
  • Frontend
  • Cloud
  • DevOps & Infrastructure

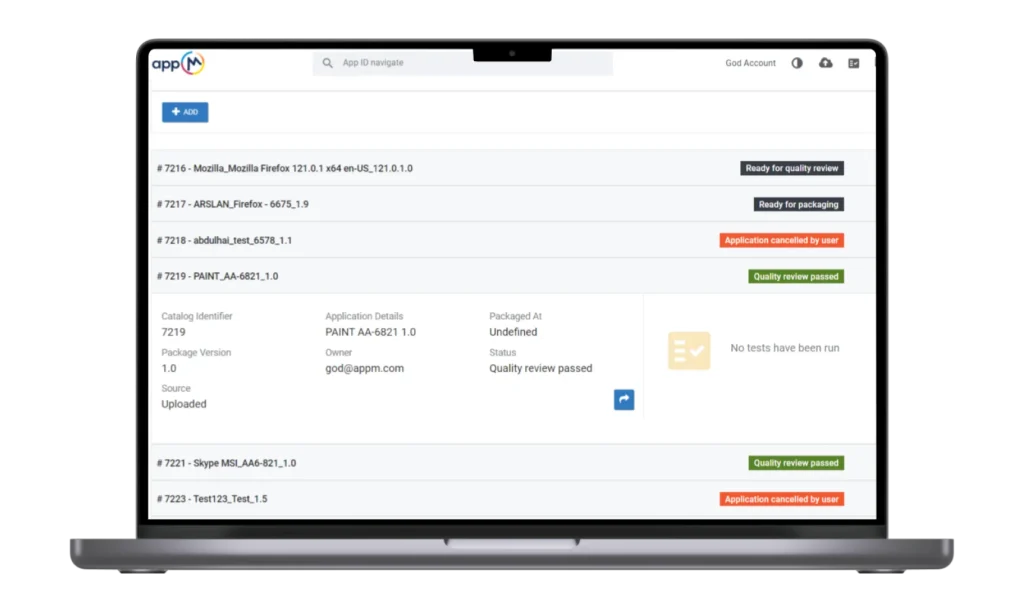
Juriba: Enterprise Digital Workplace Management Platform for Migration & Automation

An enterprise-grade automation platform that streamlines IT project workflows through smart dashboards.

Additional Info

Core Tech:
  • .NET 6
  • MS SQL
  • Redis
  • Angular
  • NgRx
  • RxJS
  • Kubernetes
  • Elasticsearch
Country:

United Kingdom United Kingdom
Testimonials

Testimonials

Carl-Fredrik Linné                                            Sweden

The solutions they’re providing is helping our business run more smoothly. We’ve been able to make quick developments with them, meeting our product vision within the timeline we set up. Listen to them because they can give strong advice about how to build good products.

Darrin Lipscomb Darrin Lipscomb
Darrin Lipscomb United States

We are a software startup and using Devox allowed us to get an MVP to market faster and less cost than trying to build and fund an R&D team initially. Communication was excellent with Devox. This is a top notch firm.

Daniel Bertuccio Daniel Bertuccio
Daniel Bertuccio Australia

Their level of understanding, detail, and work ethic was great. We had 2 designers, 2 developers, PM and QA specialist. I am extremely satisfied with the end deliverables. Devox Software was always on time during the process.

Trent Allan Trent Allan
Trent Allan Australia

We get great satisfaction working with them. They help us produce a product we’re happy with as co-founders. The feedback we got from customers was really great, too. Customers get what we do and we feel like we’re really reaching our target market.

Andy Morrey                                            United Kingdom

I’m blown up with the level of professionalism that’s been shown, as well as the welcoming nature and the social aspects. Devox Software is really on the ball technically.

Vadim Ivanenko Vadim Ivanenko
Vadim Ivanenko Switzerland

Great job! We met the deadlines and brought happiness to our customers. Communication was perfect. Quick response. No problems with anything during the project. Their experienced team and perfect communication offer the best mix of quality and rates.

Jason Leffakis Jason Leffakis
Jason Leffakis United States

The project continues to be a success. As an early-stage company, we're continuously iterating to find product success. Devox has been quick and effective at iterating alongside us. I'm happy with the team, their responsiveness, and their output.

John Boman John Boman
John Boman Sweden

We hired the Devox team for a complicated (unusual interaction) UX/UI assignment. The team managed the project well both for initial time estimates and also weekly follow-ups throughout delivery. Overall, efficient work with a nice professional team.

Tamas Pataky Tamas Pataky
Tamas Pataky Canada

Their intuition about the product and their willingness to try new approaches and show them to our team as alternatives to our set course were impressive. The Devox team makes it incredibly easy to work with, and their ability to manage our team and set expectations was outstanding.

Stan Sadokov Stan Sadokov
Stan Sadokov Estonia

Devox is a team of exepctional talent and responsible executives. All of the talent we outstaffed from the company were experts in their fields and delivered quality work. They also take full ownership to what they deliver to you. If you work with Devox you will get actual results and you can rest assured that the result will procude value.

Mark Lamb Mark Lamb
Mark Lamb United Kingdom

The work that the team has done on our project has been nothing short of incredible – it has surpassed all expectations I had and really is something I could only have dreamt of finding. Team is hard working, dedicated, personable and passionate. I have worked with people literally all over the world both in business and as freelancer, and people from Devox Software are 1 in a million.

Insights

Our Experts' Insights

7 Risks Of Outsourcing IT Services: All You Should Know

Security Best Practices In Fintech Application Development

Fortifying the Future: Ensuring Data Security in SaaS Applications

FAQ

FAQ

  • What is a vCISO, how is different from CTO, and do I need both?
    A vCISO (virtual Chief Information Security Officer) provides fractional or interim executive leadership focused on cybersecurity, risk, governance, compliance, incident readiness, and the overall security program.

    A CTO (Chief Technology Officer) typically owns the broader technology direction of the business, including architecture, engineering strategy, product technology, infrastructure decisions, and technical delivery.

    The roles overlap around areas such as cloud architecture, secure development, access controls, and technical risk, but they are accountable for different outcomes.

    Area vCISO CTO
    Primary focus Cybersecurity risk and security program leadership Technology strategy, architecture, engineering, and product delivery
    Security strategy Owns or leads Contributes and implements
    Technology roadmap Advises on security implications Typically owns
    Risk management Core responsibility Participates in technology-related risk decisions
    Compliance and governance Leads security-side requirements and readiness Supports technical implementation
    Incident response Defines governance, escalation, and executive response Supports technical containment and recovery
    Secure development Sets expectations, policies, and risk priorities Embeds them into engineering practices
    Executive reporting Reports on security posture, risk, and priorities Reports on technology performance, delivery, and strategy
    Budget focus Security controls, risk reduction, compliance, and resilience Engineering, infrastructure, platforms, and broader technology investment

    A CTO should not have to absorb every CISO responsibility on top of product, engineering, and technology leadership. A vCISO can complement the CTO by taking ownership of the security program, while the CTO and engineering organization focus on implementing the required technical controls. For smaller or growing companies, this combination can be especially practical: the business keeps its existing technology leadership while adding dedicated security expertise without hiring another full-time executive immediately.

  • What is the difference between a vCISO and a full-time CISO (vCISO vs CISO)?

    A vCISO (virtual Chief Information Security Officer) provides CISO-level security leadership on a fractional, part-time, or interim basis.

    A full-time CISO is a permanent executive dedicated to the organization and typically takes continuous ownership of its security function, team, budget, and long-term program.

    Both roles can lead security strategy, risk management, compliance, incident readiness, and executive reporting. The main differences are the engagement model, level of day-to-day involvement, cost structure, and internal ownership.

    Area vCISO Full-Time CISO
    Engagement Fractional, part-time, or interim Permanent full-time executive
    Time commitment Scaled to business needs Dedicated to the organization
    Cost structure Based on agreed scope and level of involvement Salary, benefits, incentives, recruiting, and employment overhead
    Best fit Growing companies, leadership gaps, specific security programs, or transitional periods Organizations requiring continuous dedicated security leadership
    Security strategy Leads and advises Leads and owns
    Executive reporting Provided on an agreed cadence Embedded in ongoing executive operations
    Internal team management Can guide or coordinate existing teams Typically manages the security organization directly
    Flexibility Can scale up or down as priorities change Fixed leadership capacity
    Ramp-up Can provide leadership without a full executive hiring cycle Requires recruitment, hiring, and onboarding
    Long-term ownership Can remain fractional or support transition to an internal leader Maintains ongoing internal ownership

    A vCISO can be a practical choice when you need senior security leadership but the workload, budget, or organizational stage does not yet justify a permanent CISO. It can also fill a temporary leadership gap, establish a security program, guide compliance initiatives, or prepare the organization for a future internal hire.

    A full-time CISO generally makes more sense when cybersecurity requires continuous executive attention, the organization has a substantial internal security function, or security leadership needs to be deeply embedded in daily business operations.

  • Can a vCISO help prepare for an audit or certification?

    Absolutely. A vCISO guides your organization through the preparation and execution of compliance audits, including key standards like GDPR, HIPAA, ISO 27001, or PCI-DSS. This includes conducting a detailed gap analysis, addressing deficiencies, and implementing necessary controls and documentation.

    Beyond ensuring compliance, a vCISO cost includes preparing your team for audits by streamlining processes and reducing the time and effort required, ultimately ensuring your business passes audits seamlessly and sustains compliance with confidence.

  • How quickly can we start seeing results with a vCISO?

    You’ll begin seeing value immediately, as a vCISO’s first priority is to address high-risk vulnerabilities and implement quick wins that secure your product and data. From the initial assessment, actionable steps are taken to reduce immediate threats and strengthen defenses.

    While long-term strategies such as policy refinement and system overhauls evolve over weeks or months, the early measures provide an instant boost to your security posture, ensuring tangible results from day one.

  • Is a vCISO a temporary or ongoing solution?

    A vCISO can function as either a temporary or long-term solution, tailored to your specific needs. For short-term requirements, a vCISO provides interim leadership during transitions, such as filling a gap while hiring a full-time CISO or guiding your team through immediate challenges like an audit or breach recovery.

    For ongoing needs, a vCISO offers continuous oversight, managing your cybersecurity strategy, monitoring threats, and ensuring compliance over time. This flexibility ensures the service aligns seamlessly with your organization’s timeline and evolving priorities.

  • How much does a vCISO engagement cost, and how is pricing structured?

    Pricing depends on scope, industry, and how many hours per month you need, typically a monthly retainer rather than a flat project fee, since vCISO work is ongoing advisory and leadership, not a one-time deliverable. Engagements usually start with a fixed-scope initial assessment, then move to a recurring retainer sized to your risk level and growth stage. This gives you predictable costs and the flexibility to scale hours up or down as your needs change.

  • Will a vCISO help us qualify for cyber insurance or get better rates?

    Yes. Insurers increasingly price policies based on your actual security controls: MFA coverage, incident response readiness, backup practices, and a documented, actively managed security program typically qualify you for better terms and lower premiums. Our vCISO reviews your policy application, closes the control gaps insurers flag most often, and can speak directly with your broker or underwriter if questions come up.

  • Can a vCISO specifically help us pass a SOC 2 audit?

    Yes. We map your existing controls to the SOC 2 Trust Services Criteria, close the gaps that would fail an audit, and work directly with your auditor throughout the process, this is one of the most common reasons companies bring in a vCISO. We also keep the resulting controls operational afterward, since SOC 2 requires maintaining evidence continuously, not just passing once.

Book a call

Want to Achieve Your Goals? Book Your Call Now!

Contact Us

We Fix, Transform, and Skyrocket Your Software.

Tell us where your system needs help — we’ll show you how to move forward with clarity and speed. From architecture to launch — we’re your engineering partner.

Book your free consultation. We’ll help you move faster, and smarter.

Let's Discuss Your Project!

Share the details of your project – like scope or business challenges. Our team will carefully study them and then we’ll figure out the next move together.


    By sending this form I confirm that I have read and accept the Privacy Policy

    Thank You for Contacting Us!

    We appreciate you reaching out. Your message has been received, and a member of our team will get back to you within 24 hours.

    In the meantime, feel free to follow our social.


      Thank You for Subscribing!

      Welcome to the Devox Software community! We're excited to have you on board. You'll now receive the latest industry insights, company news, and exclusive updates straight to your inbox.