Code Quality Audit Services

Let's Talk
  • IDENTIFY BOTTLENECKS
    Uncover performance issues and inefficient code paths that restrain development and degrade user experience

  • ELIMINATE TECHNICAL DEBT
    With exposed legacy architecture, poor patterns, and shortcuts, you’ll get your codebase cleaned up and reduce long-term maintenance costs

  • FUTURE-PROOF YOUR CODEBASE
    Ensure your system is ready for growth. We align your architecture and code quality with modern standards, making it easier to adopt new features and technologies

Why It Matters

From abstraction to numbers — learn how to transform your software into a maintainable, scalable, and performant solution before fundamental adjustments are made.

Code audit services ensure your code is compliant and effective, prepared for future development:

  • Reduced maintenance costs by detecting technical debt and redundant logic,
  • Early detection of security vulnerabilities,
  • Improved team productivity with cleaner, more readable code,
  • A foundation for smooth modernization, microservices migration, or re-architecture,
  • Insights into architecture improvements and integration opportunities.

Modernizing unstable systems? Launching new products?

We build development environments that deliver enterprise-grade scalability, compliance-driven security, and control baked in from day one.

Check Our Portfolio
What We Offer

Code Audit Services We Provide

Code audit services are a structured review of an existing codebase to identify issues affecting quality, security, performance, maintainability, scalability, and technical debt. They typically cover architecture, coding standards, dependencies, test coverage, vulnerabilities, duplicated logic, and upgrade risks, ending with prioritized findings and a practical remediation roadmap.

  • Code Security Audit

    To ensure your application is secure, a comprehensive code security audit that goes beyond surface-level checks is essential. Thus, we review critical security mechanisms:

    • auditing and logging,
    • input and data validation,
    • code obfuscation,
    • thread safety, session management,
    • serialization filtering,
    • communication channels,
    • input/output operations,
    • connection strings.

    During the source code security audit, we identify vulnerabilities including race conditions, buffer overflows, code injections, cross-site scripting (XSS), and encryption flaws, helping you close security gaps before they become risks.
  • Legacy Code and Architecture Review

    Outdated systems pose a risk. But before the modernization, we can help you audit code and assess monolithic applications as a foundation for microservice transitions, and recommend re-architecture strategies tailored to your business goals.

    We thoroughly analyze monolithic applications to identify areas of:

    • tight coupling,
    • redundant logic,
    • obsolete dependencies.

    Based on your business objectives, we recommend the most cost-efficient and applicable modernization strategy. It could be refactoring, full re-architecture, or a phased migration to microservices.

    We also assess whether your system is ready for cloud environments and deliver a robust plan for a future-proof architecture. The architecture, recommended through our software code audit service, supports scalability, agility, and long-term growth.

  • End-to-End Performance and Maintainability Check

    In the process of a comprehensive code audit, we examine how well your code performs under real-world conditions. You get a prioritized roadmap for fixing inefficiencies, improving modularity, and enhancing code readability:

    • a check for clear, descriptive variable names and meaningful code comments,
    • preparation of a well-maintained documentation,
    • evaluation of the use of frameworks and reusable components,
    • assessment of proper code splitting and portability across environments.

    Our team also reviews version control hygiene, exception-handling strategies, and the integration of linter tools to enforce coding standards and reduce technical debt.

Our Process

How We Work

01.

01. Planning & Scope Definition

The better we understand your goals and development context, the better we can select the proper code audit strategy. Whether you're aiming to modernize a legacy system, prepare for a cloud migration, or improve delivery speed, the plan, as well as the evaluation criteria, will differ.

02.

02. Environment & Codebase Preparation

Before diving into analysis, we prepare the codebase for audit by verifying that all relevant repositories and dependencies are accessible. We also gather and explore supporting documentation to understand the logic, architecture, and any known technical challenges.

03.

03. Code Analysis & Manual Review

A two-layer analysis, static and dynamic, detects bugs, security vulnerabilities, code smells, and complexity issues. Then, our senior engineers perform a manual review of critical areas, assessing architecture, design patterns, naming, modularity, and overall code health. In the end, we also check quality indicators like Cyclomatic Complexity and Maintainability Index, moving away from guesswork. In parallel with the code review, we examine the architecture for risks and inefficiencies and audit session management, input validation, serialization filters, and communication channels. All is to uncover vulnerabilities like XSS, injection flaws, or unsafe cryptographic practices.

04.

04. Dependency and Open-Source Risk Review

Assess third-party libraries, frameworks, packages, and other open-source components for known vulnerabilities, outdated versions, unsupported dependencies, and licensing concerns. The review include Software Composition Analysis (SCA), dependency inventory, vulnerable package identification, license checks, and Software Bill of Materials (SBOM) preparation where relevant. The goal is to identify external risks that are easy to miss in a source-code review and give engineering teams a clearer plan for upgrading, replacing, or containing problematic dependencies.

05.

05. Test Coverage and Quality Engineering Review

Evaluate the existing test strategy as a separate part of the audit, including unit, integration, API, end-to-end, and regression coverage where applicable. The review can assess test depth, critical-path coverage, test reliability, automation gaps, flaky tests, and how effectively tests support refactoring or modernization. The outcome is a clearer understanding of where insufficient test coverage creates release or modernization risk, along with prioritized recommendations for strengthening the quality safety net.

06.

06. Security Findings Mapped to OWASP, CWE

Classify security-related findings using recognized references such as the OWASP Top 10 and CWE where applicable, so vulnerabilities are easier to understand, compare, and remediate. Severity scoring based on an agreed methodology to distinguish critical risks from lower-priority issues should connect each finding with evidence, affected components, potential impact, remediation guidance, and severity so engineering and security teams can prioritize work more consistently.

07.

07. Reporting & Recommendations

A structured code audit report is always backed up with a summary of findings, categorized issue lists, and recommendations on further actions. It could be targeted refactoring, updates, re-architecture, or development workflow improvements. We also suggest how to improve long-term KPIs to guarantee impeccable protection.

  • 01. Planning & Scope Definition

  • 02. Environment & Codebase Preparation

  • 03. Code Analysis & Manual Review

  • 04. Dependency and Open-Source Risk Review

  • 05. Test Coverage and Quality Engineering Review

  • 06. Security Findings Mapped to OWASP, CWE

  • 07. Reporting & Recommendations

Benefits

Value We Provide

01

Quality Excellence

Our Project Management (PMO), Business Analysis (BAO), and Quality Management (QMO) offices form an audit code of conduct according to the ISO 9001, ISO 27001, HIPAA, and GDPR standards, overseeing every project delivery stage. Together, they ensure confident planning, smooth development, and efficient deployment, removing team friction.

02

Shorter Timelines

Thanks to our AI Solution Accelerator™, automated testing, and static code analysis, we deliver high-quality results up to 30% faster than the industry average. In all stages of software code audit, our focus is always on precision, speed, and long-term business impact for your company.

03

Proven Expertise

We leverage the advanced static code analyzers and profilers to identify slow queries and bottlenecks, whether it’s a website code audit or PHP code auditing. To fine-tune performance and memory usage, we rely on potent tools, ensuring your system runs efficiently under real-world conditions.

04

KPI-Based Approach

Turning from guesswork to frameworks, our audits are driven by measurable code audit service indicators such as Cyclomatic Complexity and the Maintainability Index. Beyond code-level metrics, we connect findings to delivery metrics like cycle time, deployment frequency, and change failure rate.

Case Studies

Our Latest Works

View All Case Studies
Web 3 White-label PaaS NeoBank Web 3 White-label PaaS NeoBank
  • Web3
  • Fintech

Web3 PaaS Ecosystem for Next-Gen NeoBanking, RegTech, and Secure Data Vaulting

A blockchain-powered PaaS ecosystem enabling financial providers to launch custom neobanking solutions with secure infrastructure.

Additional Info

Core Tech:
  • Blockchain
  • .NET
  • Node.js
  • AWS
  • Docker
  • PostgreSQL
  • React Native
Country:

USA USA

AI-Driven Content Personalization for a Leading Sports Media Platform AI-Driven Content Personalization for a Leading Sports Media Platform

AI-Driven Content Personalization for a Leading Sports Media Platform

AI-driven content personalization engine for a global sports media platform delivering real-time coverage, automated article generation, and fan-tailored news feeds.

Additional Info

Core Tech:
  • Next.js 14
  • .NET 8 APIs
  • Python (FastAPI, GPT-4.1, spaCy/HF Transformers)
  • PostgreSQL + pgvector
  • Kafka/Redpanda
  • Redis
  • Qdrant
  • AKS (Azure Kubernetes)
  • Argo CD
Country:

Switzerland Switzerland

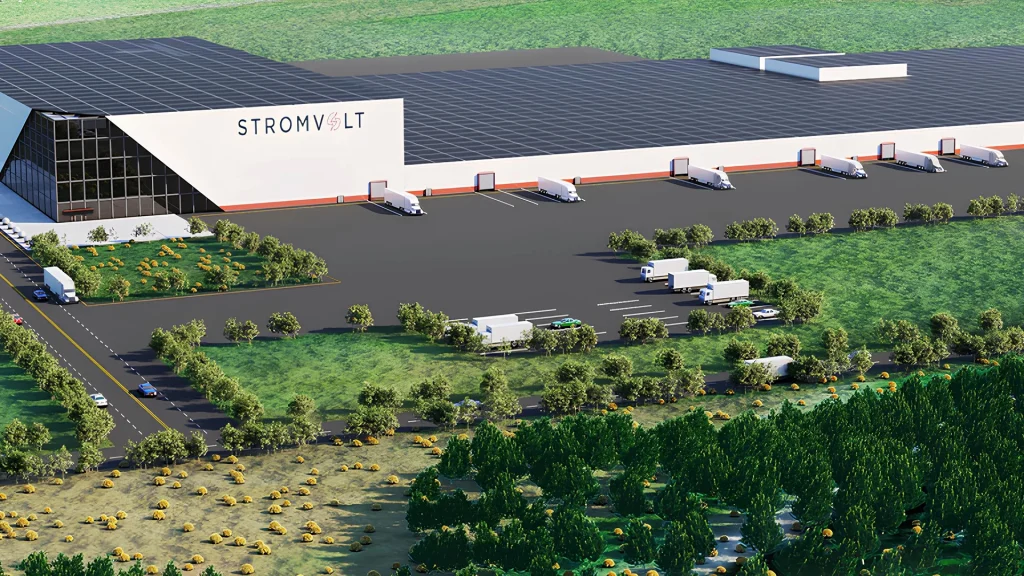
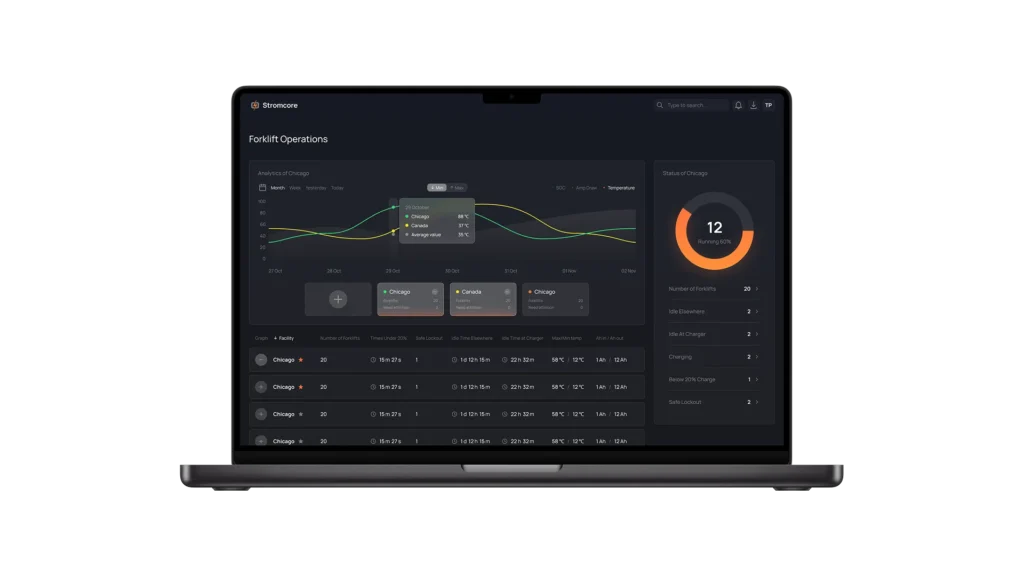
Stromcore Stromcore

Stromcore: Web Interface for Real-Time Battery Monitoring in a PaaS Logistics Platform

A web interface enabling real-time forklift battery tracking and predictive maintenance scheduling.

Additional Info

Core Tech:
  • React
  • TypeScript
  • Node.js
  • GraphQL
  • AWS
Country:

Canada Canada
Testimonials

Testimonials

Carl-Fredrik Linné                                            Sweden

The solutions they’re providing is helping our business run more smoothly. We’ve been able to make quick developments with them, meeting our product vision within the timeline we set up. Listen to them because they can give strong advice about how to build good products.

Darrin Lipscomb Darrin Lipscomb
Darrin Lipscomb United States

We are a software startup and using Devox allowed us to get an MVP to market faster and less cost than trying to build and fund an R&D team initially. Communication was excellent with Devox. This is a top notch firm.

Daniel Bertuccio Daniel Bertuccio
Daniel Bertuccio Australia

Their level of understanding, detail, and work ethic was great. We had 2 designers, 2 developers, PM and QA specialist. I am extremely satisfied with the end deliverables. Devox Software was always on time during the process.

Trent Allan Trent Allan
Trent Allan Australia

We get great satisfaction working with them. They help us produce a product we’re happy with as co-founders. The feedback we got from customers was really great, too. Customers get what we do and we feel like we’re really reaching our target market.

Andy Morrey                                            United Kingdom

I’m blown up with the level of professionalism that’s been shown, as well as the welcoming nature and the social aspects. Devox Software is really on the ball technically.

Vadim Ivanenko Vadim Ivanenko
Vadim Ivanenko Switzerland

Great job! We met the deadlines and brought happiness to our customers. Communication was perfect. Quick response. No problems with anything during the project. Their experienced team and perfect communication offer the best mix of quality and rates.

Jason Leffakis Jason Leffakis
Jason Leffakis United States

The project continues to be a success. As an early-stage company, we're continuously iterating to find product success. Devox has been quick and effective at iterating alongside us. I'm happy with the team, their responsiveness, and their output.

John Boman John Boman
John Boman Sweden

We hired the Devox team for a complicated (unusual interaction) UX/UI assignment. The team managed the project well both for initial time estimates and also weekly follow-ups throughout delivery. Overall, efficient work with a nice professional team.

Tamas Pataky Tamas Pataky
Tamas Pataky Canada

Their intuition about the product and their willingness to try new approaches and show them to our team as alternatives to our set course were impressive. The Devox team makes it incredibly easy to work with, and their ability to manage our team and set expectations was outstanding.

Stan Sadokov Stan Sadokov
Stan Sadokov Estonia

Devox is a team of exepctional talent and responsible executives. All of the talent we outstaffed from the company were experts in their fields and delivered quality work. They also take full ownership to what they deliver to you. If you work with Devox you will get actual results and you can rest assured that the result will procude value.

Mark Lamb Mark Lamb
Mark Lamb United Kingdom

The work that the team has done on our project has been nothing short of incredible – it has surpassed all expectations I had and really is something I could only have dreamt of finding. Team is hard working, dedicated, personable and passionate. I have worked with people literally all over the world both in business and as freelancer, and people from Devox Software are 1 in a million.

FAQ

Frequently Asked Questions

  • What is a code quality audit, and why is it important?

    A code quality audit is an in-depth review of a software codebase. Its purpose is to evaluate how well the code does its job — how legible, consistent, and maintainable it is. Cleaner code carries less technical debt and fewer productivity issues, so the system stays scalable and secure as it grows. So the system remains scalable and secure as it grows.

  • How do you perform a code quality audit?

    Code quality audits typically combine several methods to ensure thorough analysis. The schema is the following.

    Coding audit software like Coverity, and ReSharper automatically scans source code to detect syntax errors, security vulnerabilities, and code smells. It’s the first step.

    Then, static analysis examines code, helping to identify unused variables and dead code via SpotBugs, PMD, and CheckStyle. Dynamic analysis runs the code and reveals runtime problems that appear in the process. It could be memory leaks, race conditions, and concurrency issues.

    Additionally, peer reviews come in handy. Here, other developers manually inspect code for readability, adherence to standards, and overall quality. Together, these steps give a complete picture of code quality.

  • What tools are best to audit code?

    Some of the best automatic apps include SonarQube, ESLint, Pylint, Checkstyle, and CodeClimate. They analyze code for bugs, complexity thresholds, and style violations. Plus, IDE-integrated tools and test coverage analyzers like JaCoCo or Istanbul are also handy and deliver deeper insights.

  • How can I identify and reduce technical debt through a code audit?

    Technical debt, like messy code, lack of tests, outdated libraries, or patchwork fixes, can be identified through automatic and manual checks. Furthermore, the uncovered debt is managed and eliminated by code refactoring, simplifying logic, improving tests, and implementing better development practices. This pairs closely with our Quality Control Management Services. For more on this, explore our product audit services.

  • What are the common issues found during a code quality audit?

    Common issues of poor code include inconsistent naming, high code complexity, duplicates, tightly coupled components, lack of documentation or tests, performance bottlenecks, and unaddressed security concerns. These problems typically result from rushed development, poor planning, or a lack of proper code review processes — all of which can be identified through a code quality audit. This pairs closely with our Quality Control Management Services.

Book a call

Want to Achieve Your Goals? Book Your Call Now!

Contact Us

We Fix, Transform, and Skyrocket Your Software.

Tell us where your system needs help — we’ll show you how to move forward with clarity and speed. From architecture to launch — we’re your engineering partner.

Book your free consultation. We’ll help you move faster, and smarter.

Let's Discuss Your Project!

Share the details of your project – like scope or business challenges. Our team will carefully study them and then we’ll figure out the next move together.


    By sending this form I confirm that I have read and accept the Privacy Policy

    Thank You for Contacting Us!

    We appreciate you reaching out. Your message has been received, and a member of our team will get back to you within 24 hours.

    In the meantime, feel free to follow our social.


      Thank You for Subscribing!

      Welcome to the Devox Software community! We're excited to have you on board. You'll now receive the latest industry insights, company news, and exclusive updates straight to your inbox.